Helps you collect audit evidence for ISO 27001, SOC 2 and PCI-DSS. Centralize RADIUS, Syslog, CLI commands, and Apprise multi-channel alerts, backed by an AI Copilot with complete tool execution auditability.
Unifies 5 distinct forensic logging layers into a single centralised, searchable audit repository:
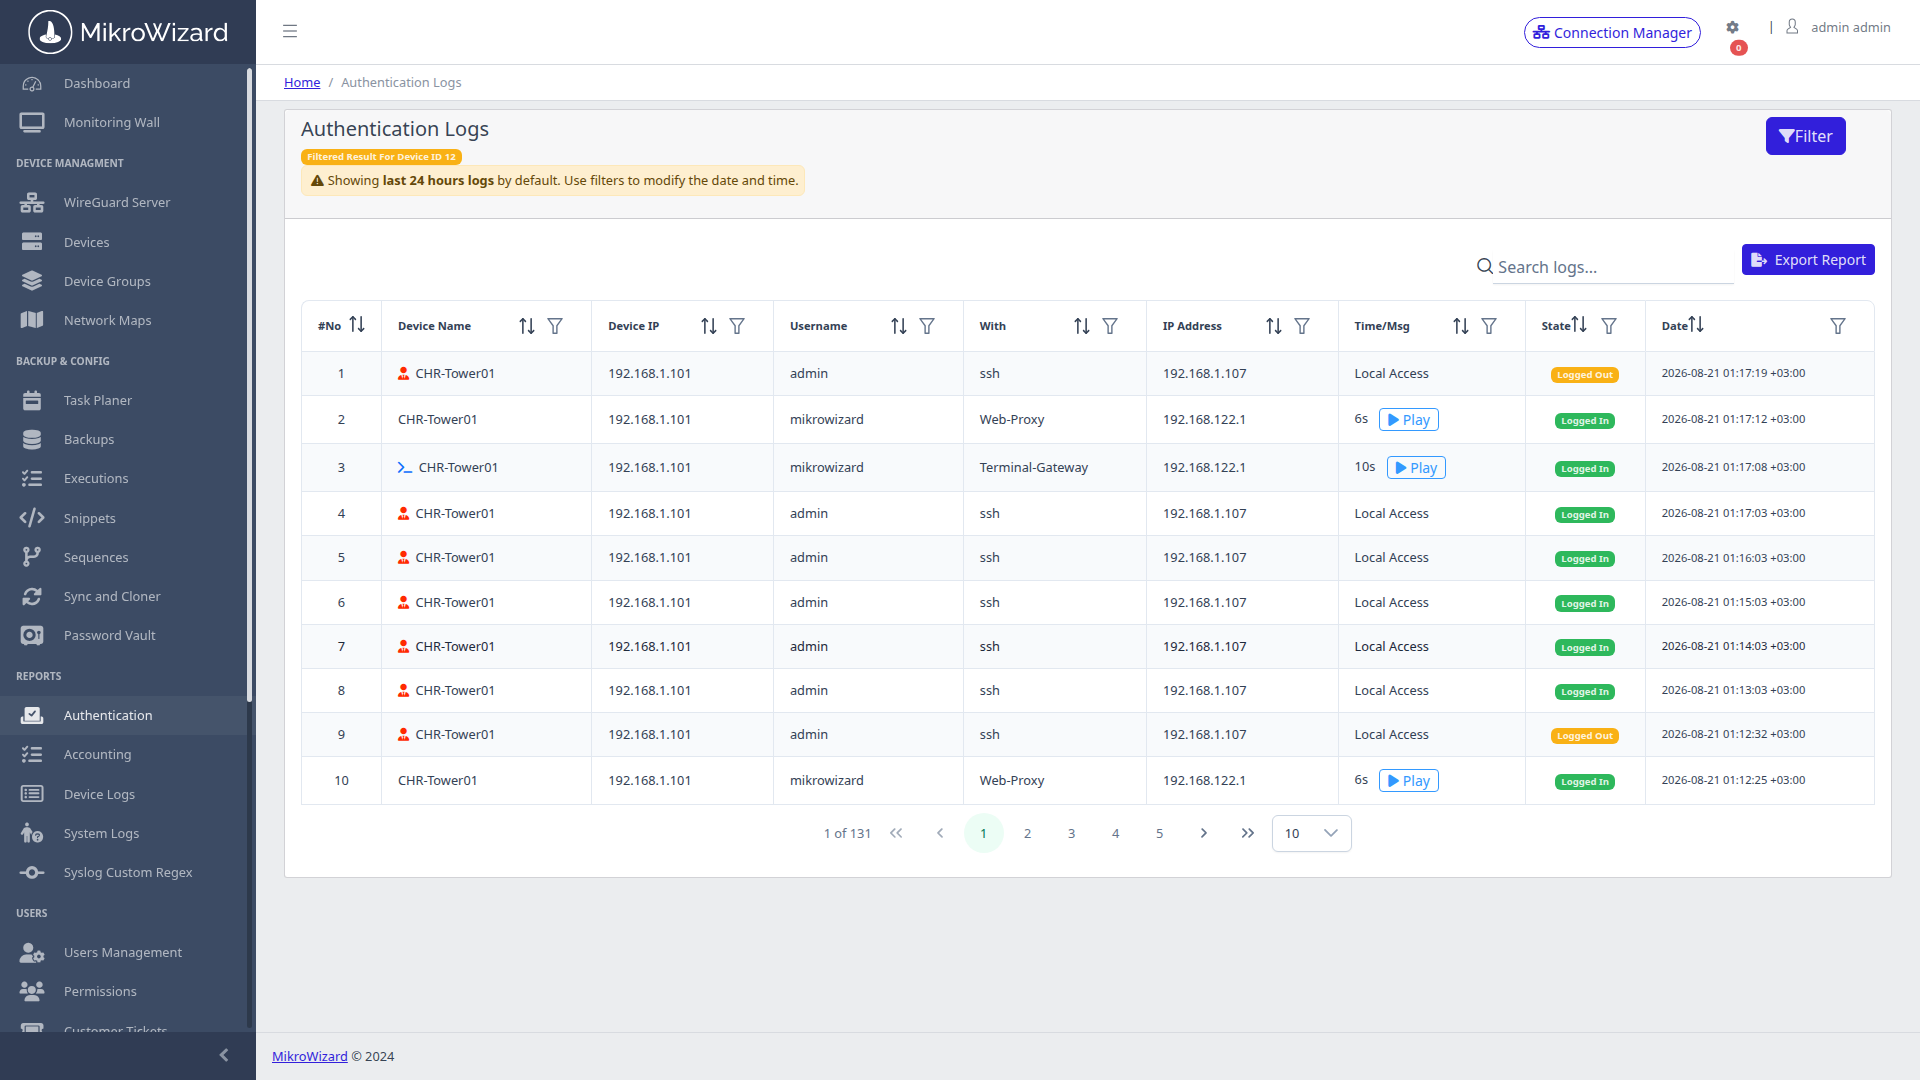
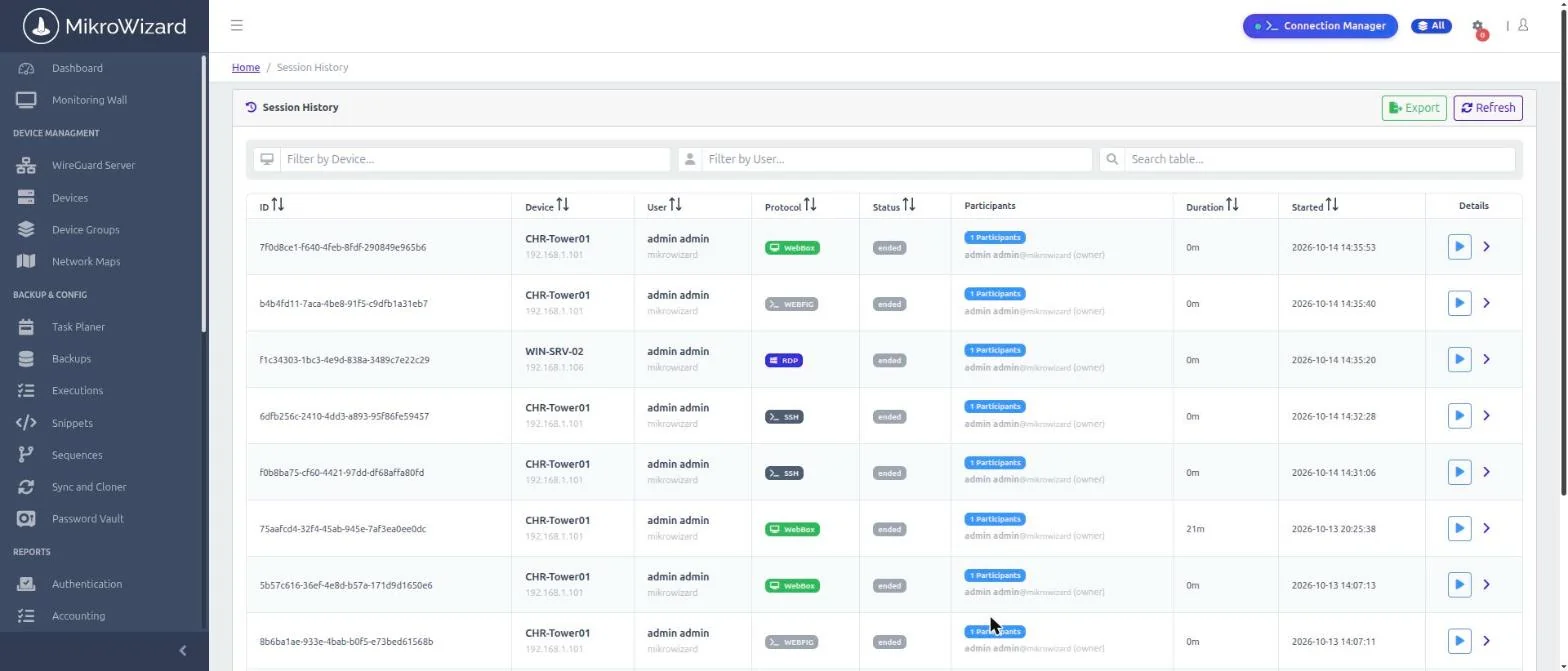
Privileged access management (PAM) for network devices and servers needs one audit trail, whatever the protocol. Since MikroWizard 2.1.0, SSH, Telnet, RDP, VNC, WebBox and WebFig sessions are all recorded and can be replayed in the browser.
RDP, VNC and WebBox need the Terminal Gateway addon (v1.3.0). RDP and VNC work with any Windows or Linux host; WebBox is for MikroTik devices. Read the 2.1.0 release post →
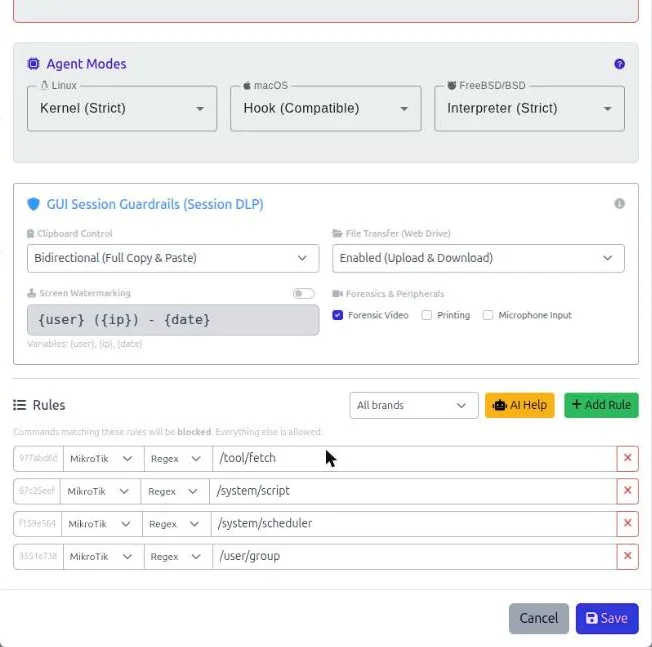
Session DLP policies decide what an operator can do inside a remote session, and how much evidence is kept.
Choose how long audit and monitoring data is kept; the default is 365 days. Unresolved events and logins that have recordings are always kept, so open issues and recorded sessions are never cleaned up by retention.
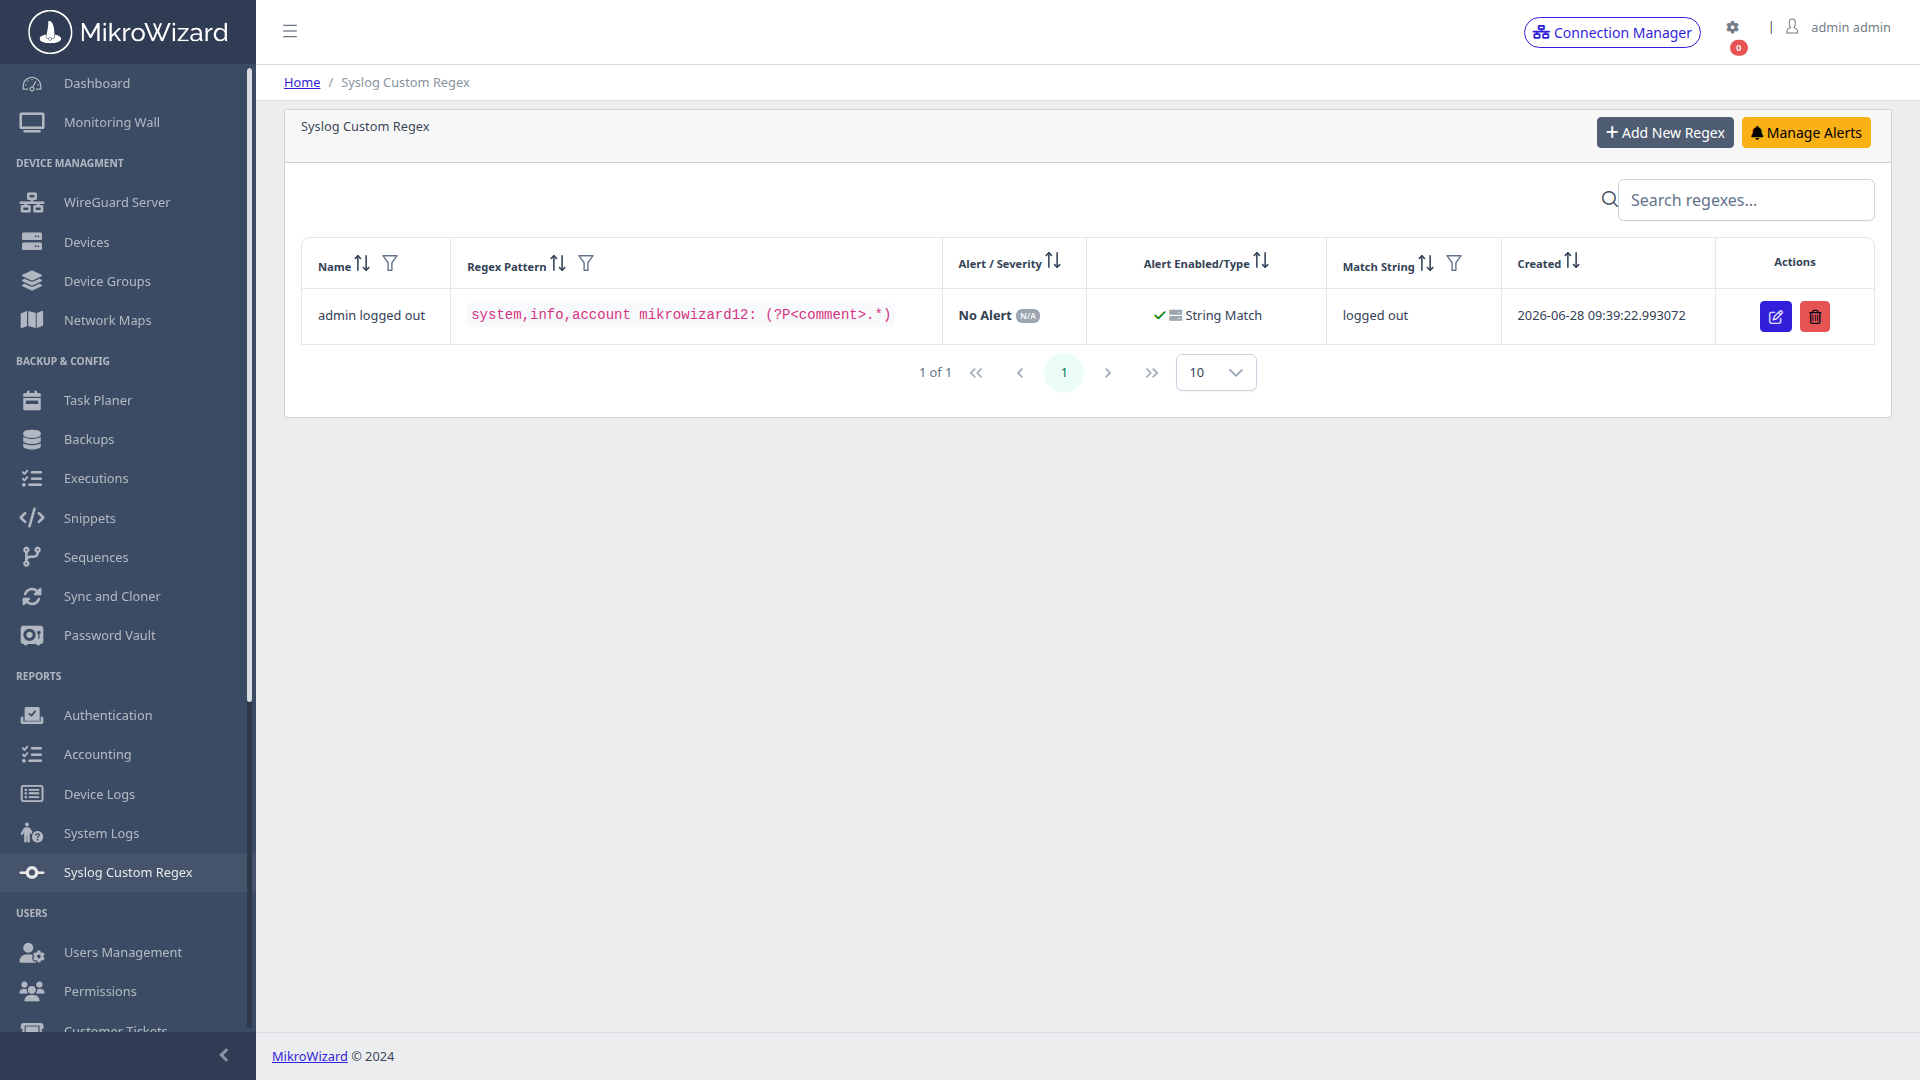
Transform millions of noisy router syslog messages into actionable operational insights. Define custom regex patterns to classify critical events:
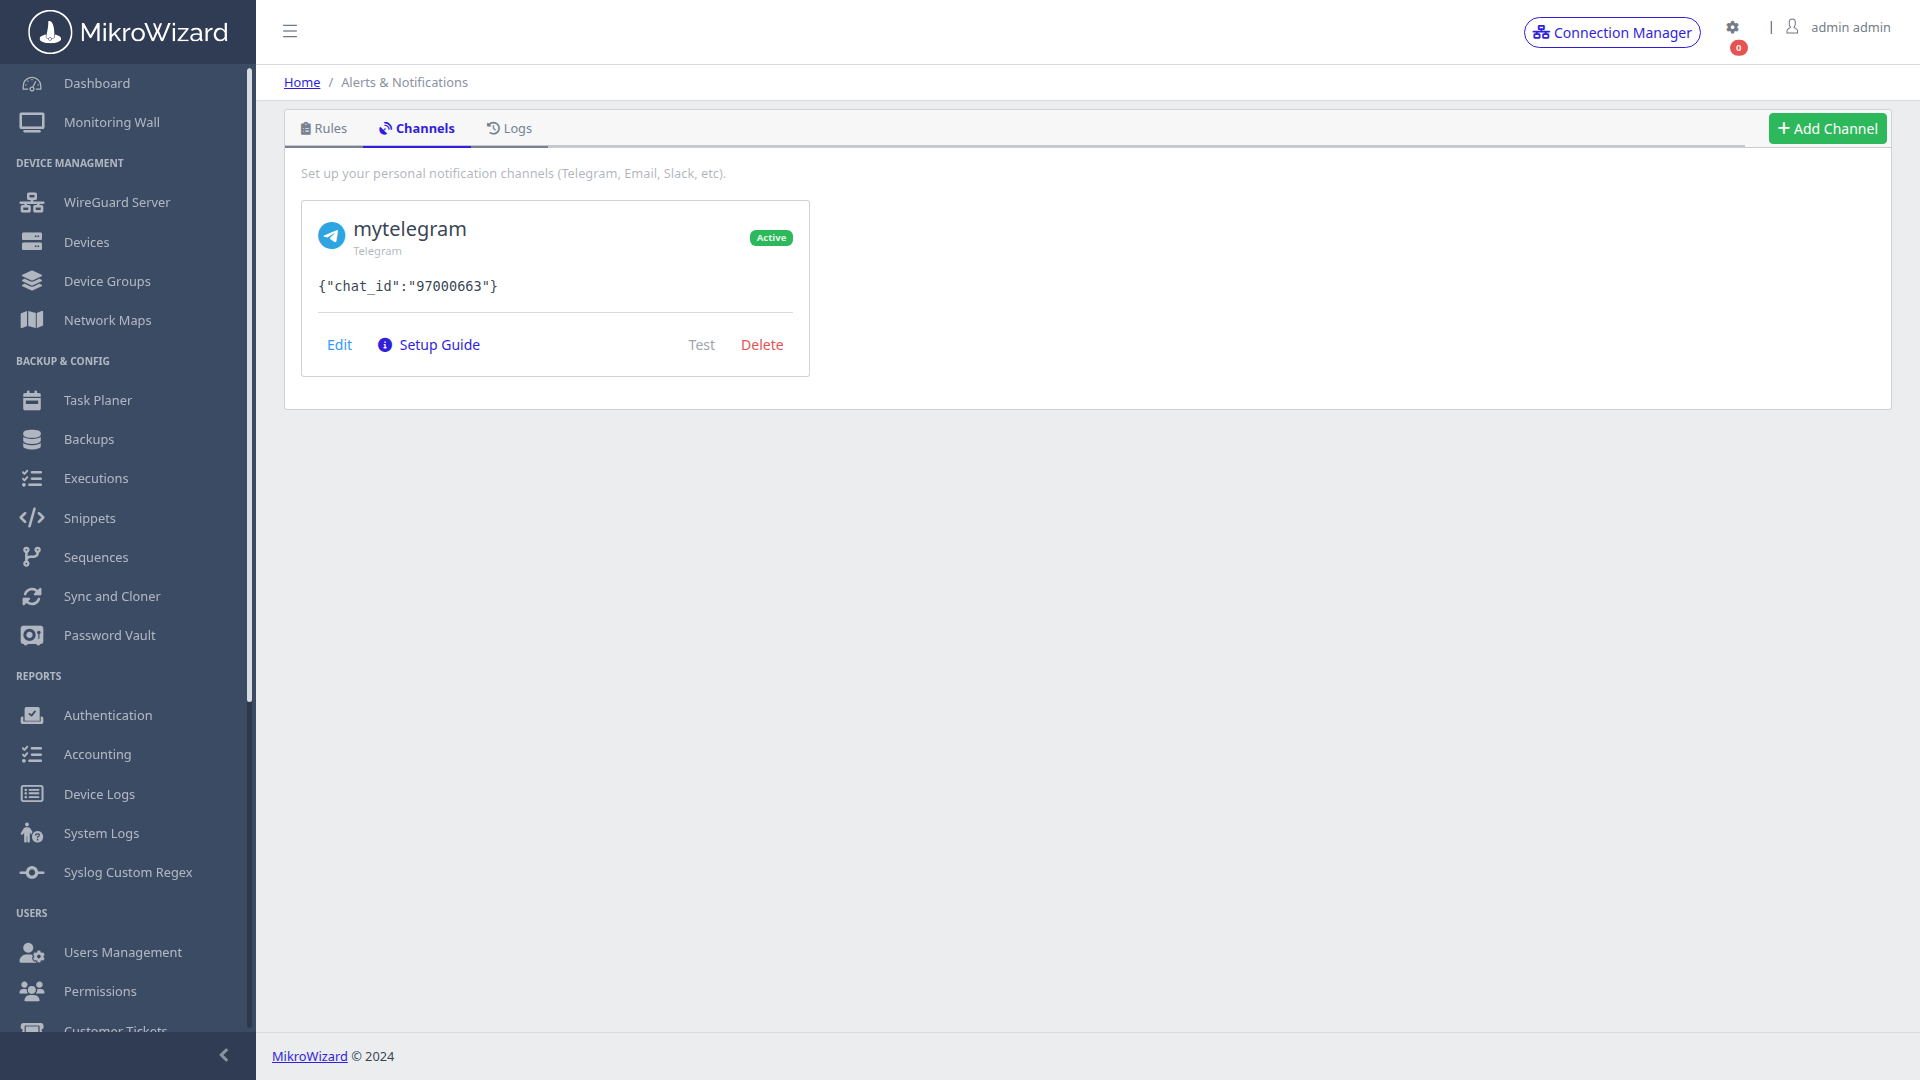
Ensure critical network incidents reach on-call engineers within seconds. MikroWizard integrates Apprise, with 11 built-in channels plus any Apprise URL:
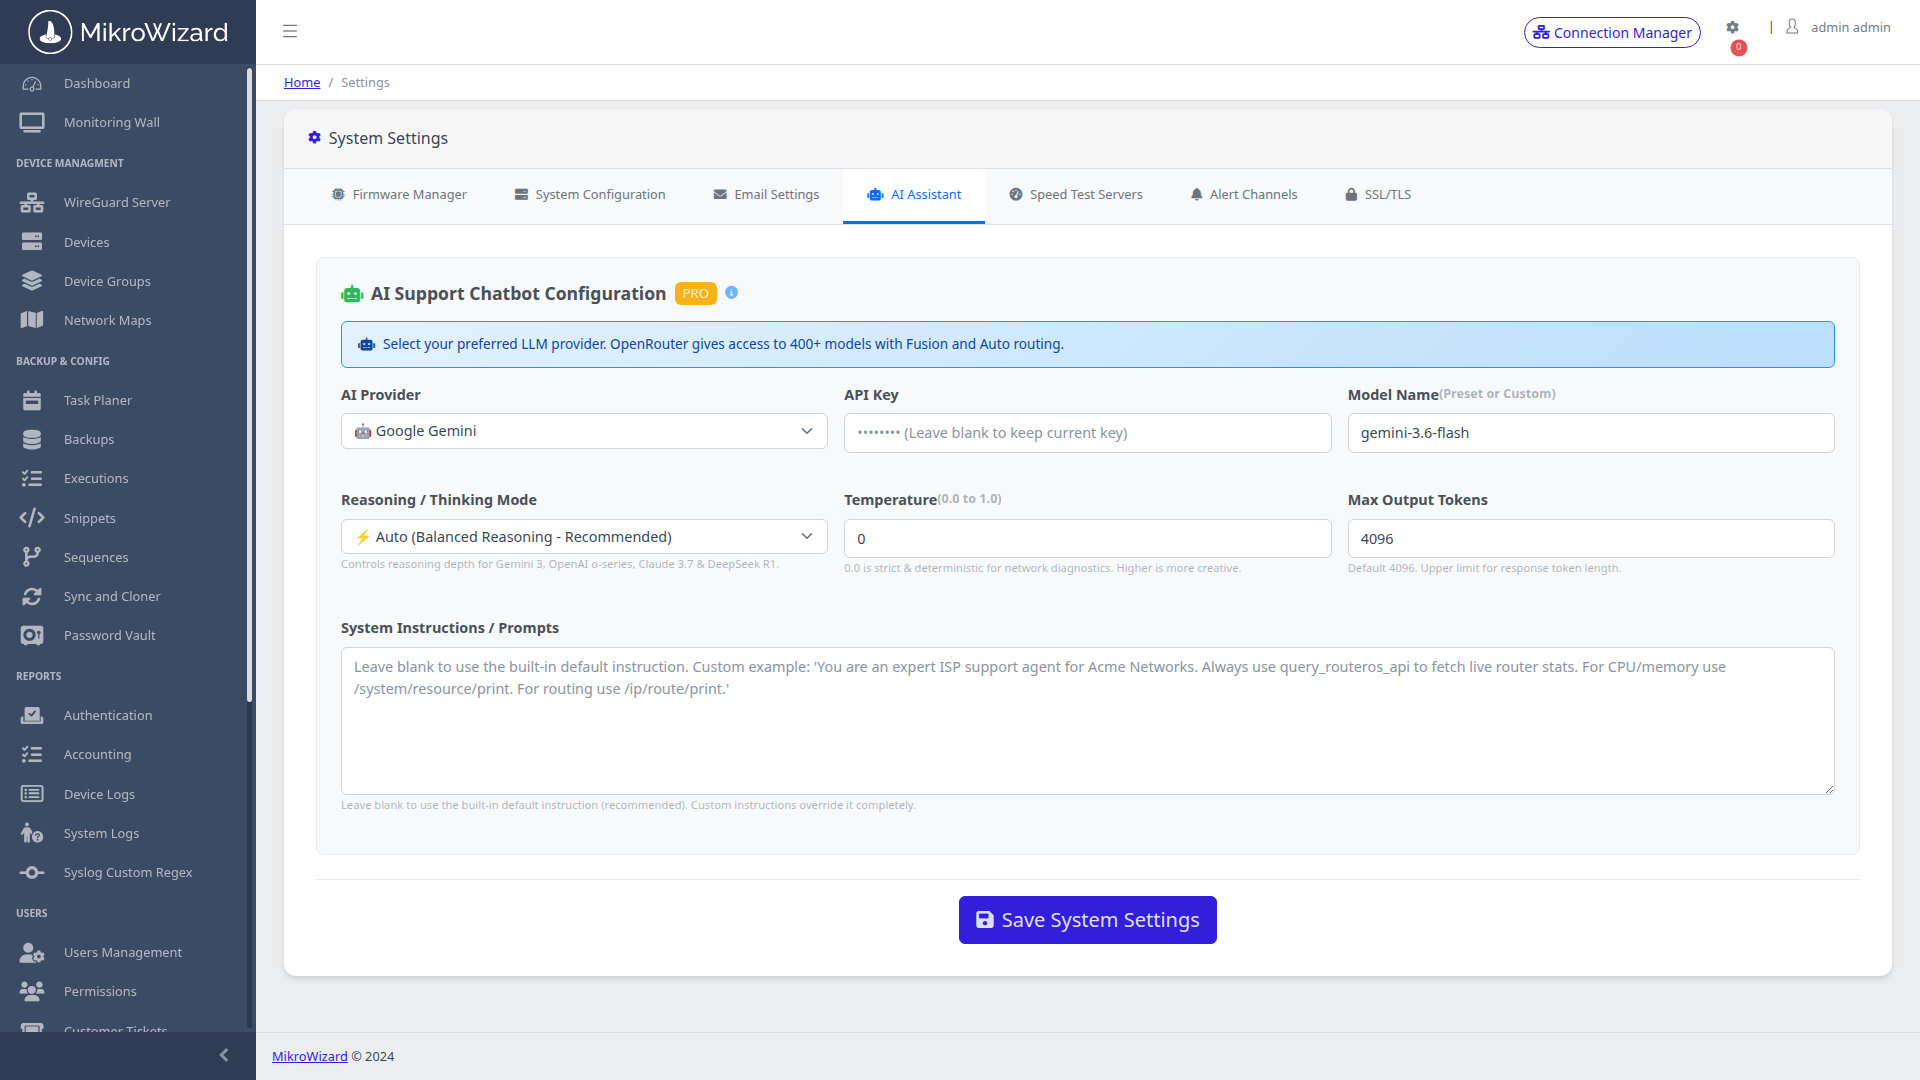
Accelerate incident root-cause analysis with an AI assistant that understands network topology and RouterOS syntax. Supports Google Gemini, OpenAI, Anthropic Claude, DeepSeek and OpenRouter via a unified LLM abstraction layer.
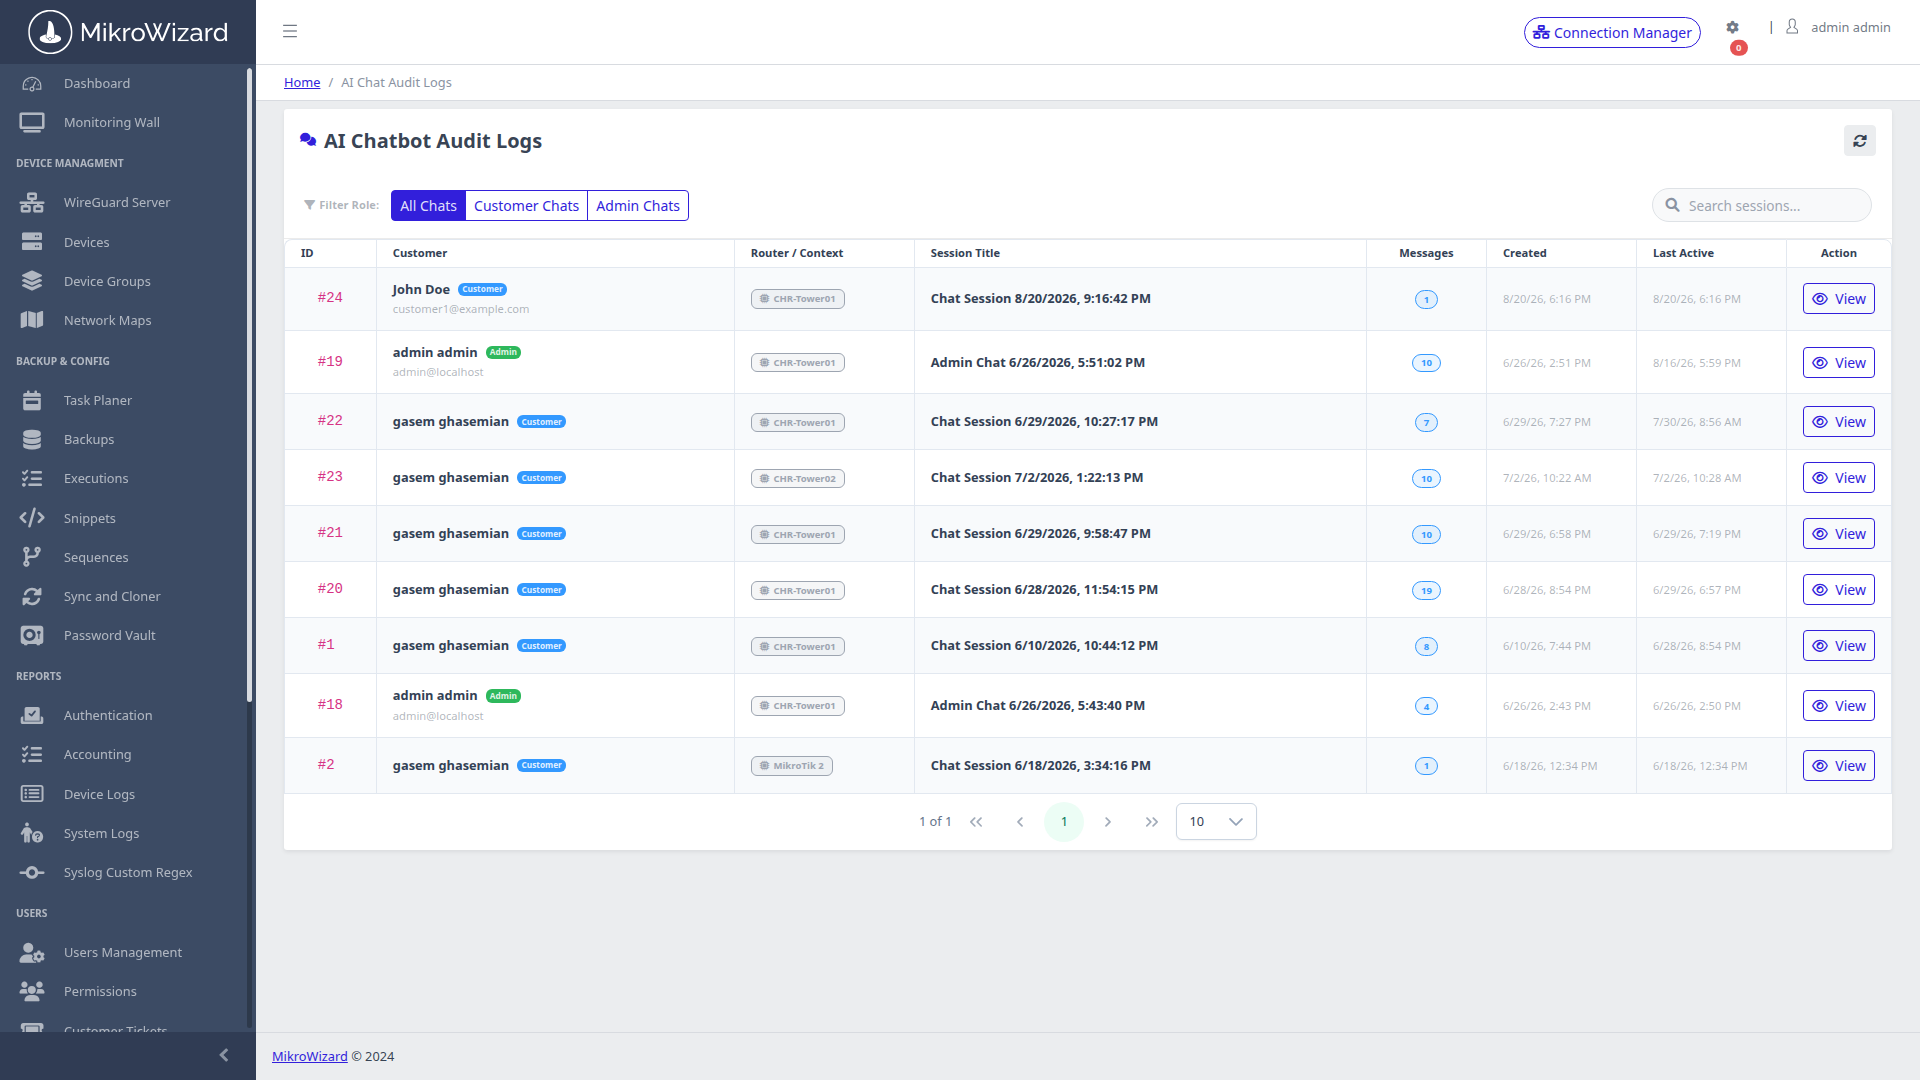
Enterprise AI safety, explainability, and governance — every AI interaction is logged in a centralised, searchable audit trail. Satisfy security auditors who need complete visibility into what the AI assistant did, why, and on which routers.
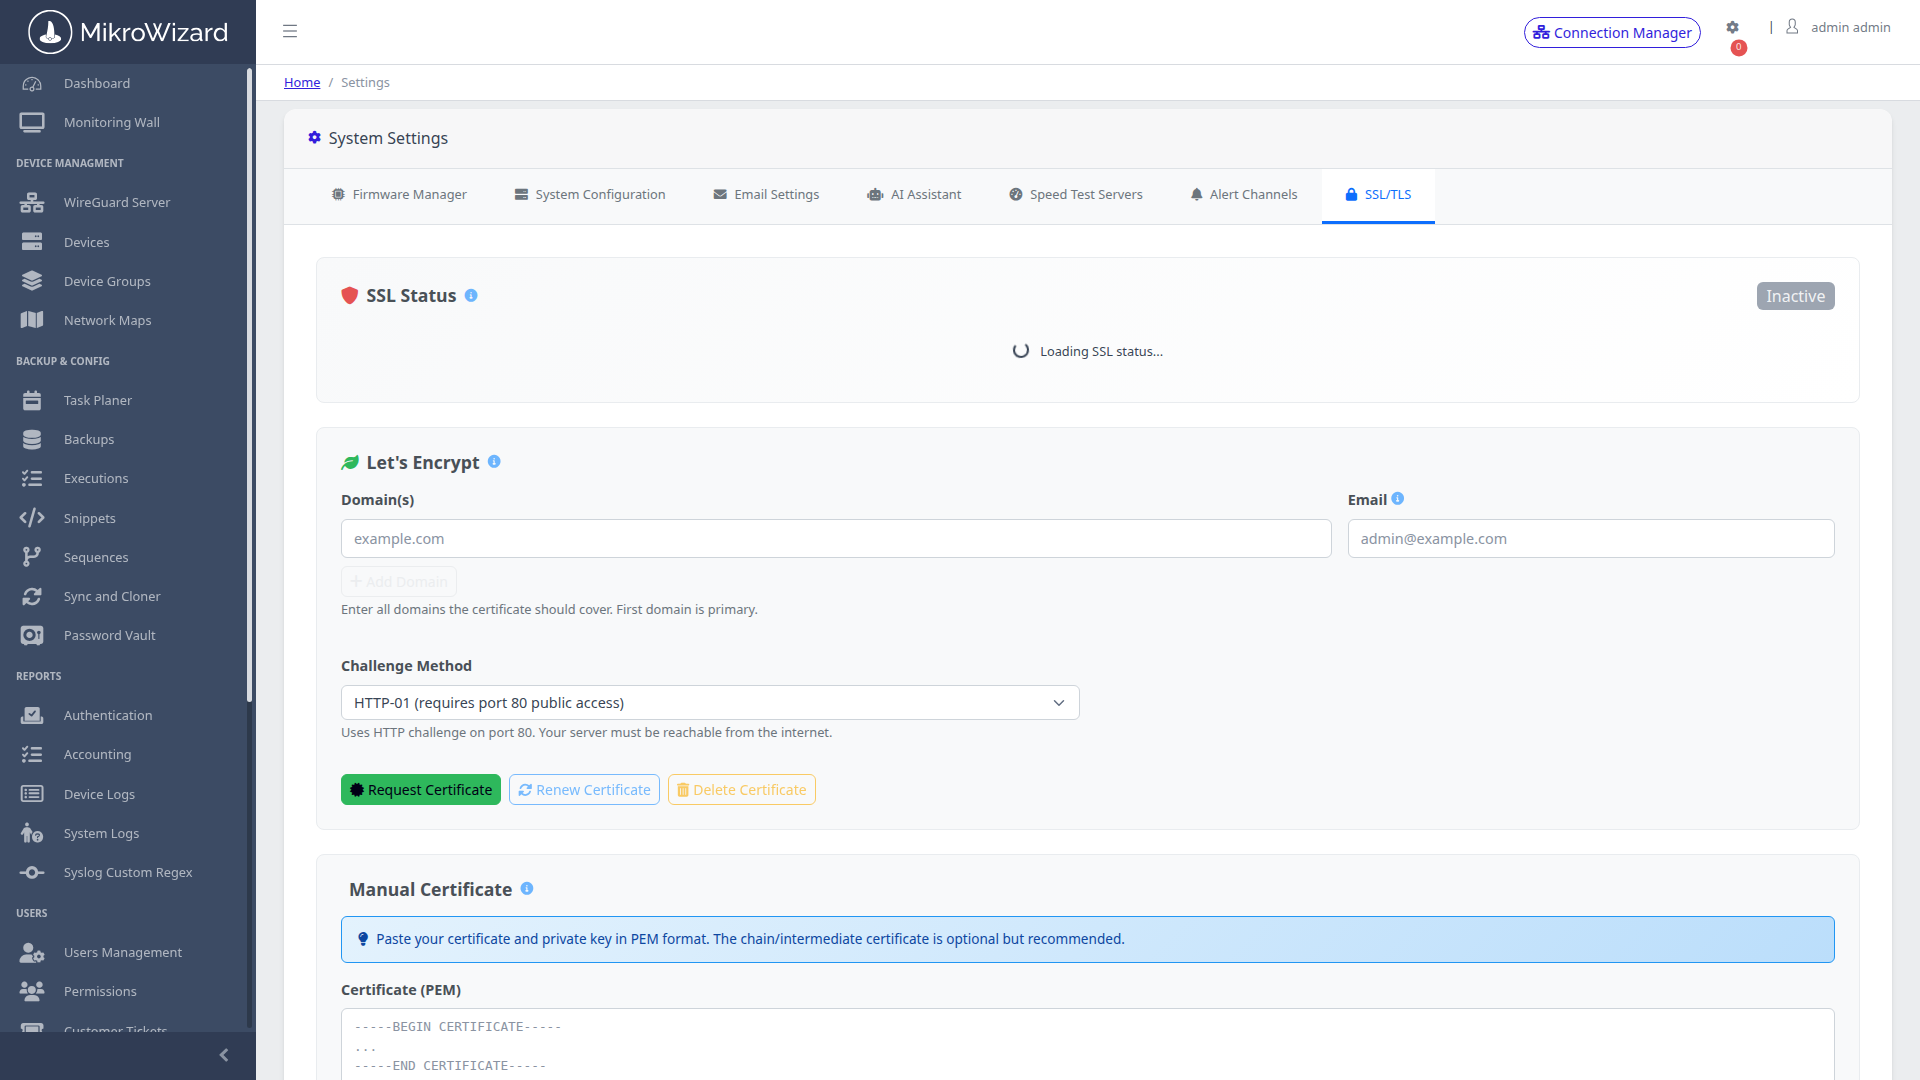
Zero-touch HTTPS encryption for the entire management portal. MikroWizard automates the ACME HTTP-01 challenge verification for Let's Encrypt certificates, eliminating manual renewal headaches.
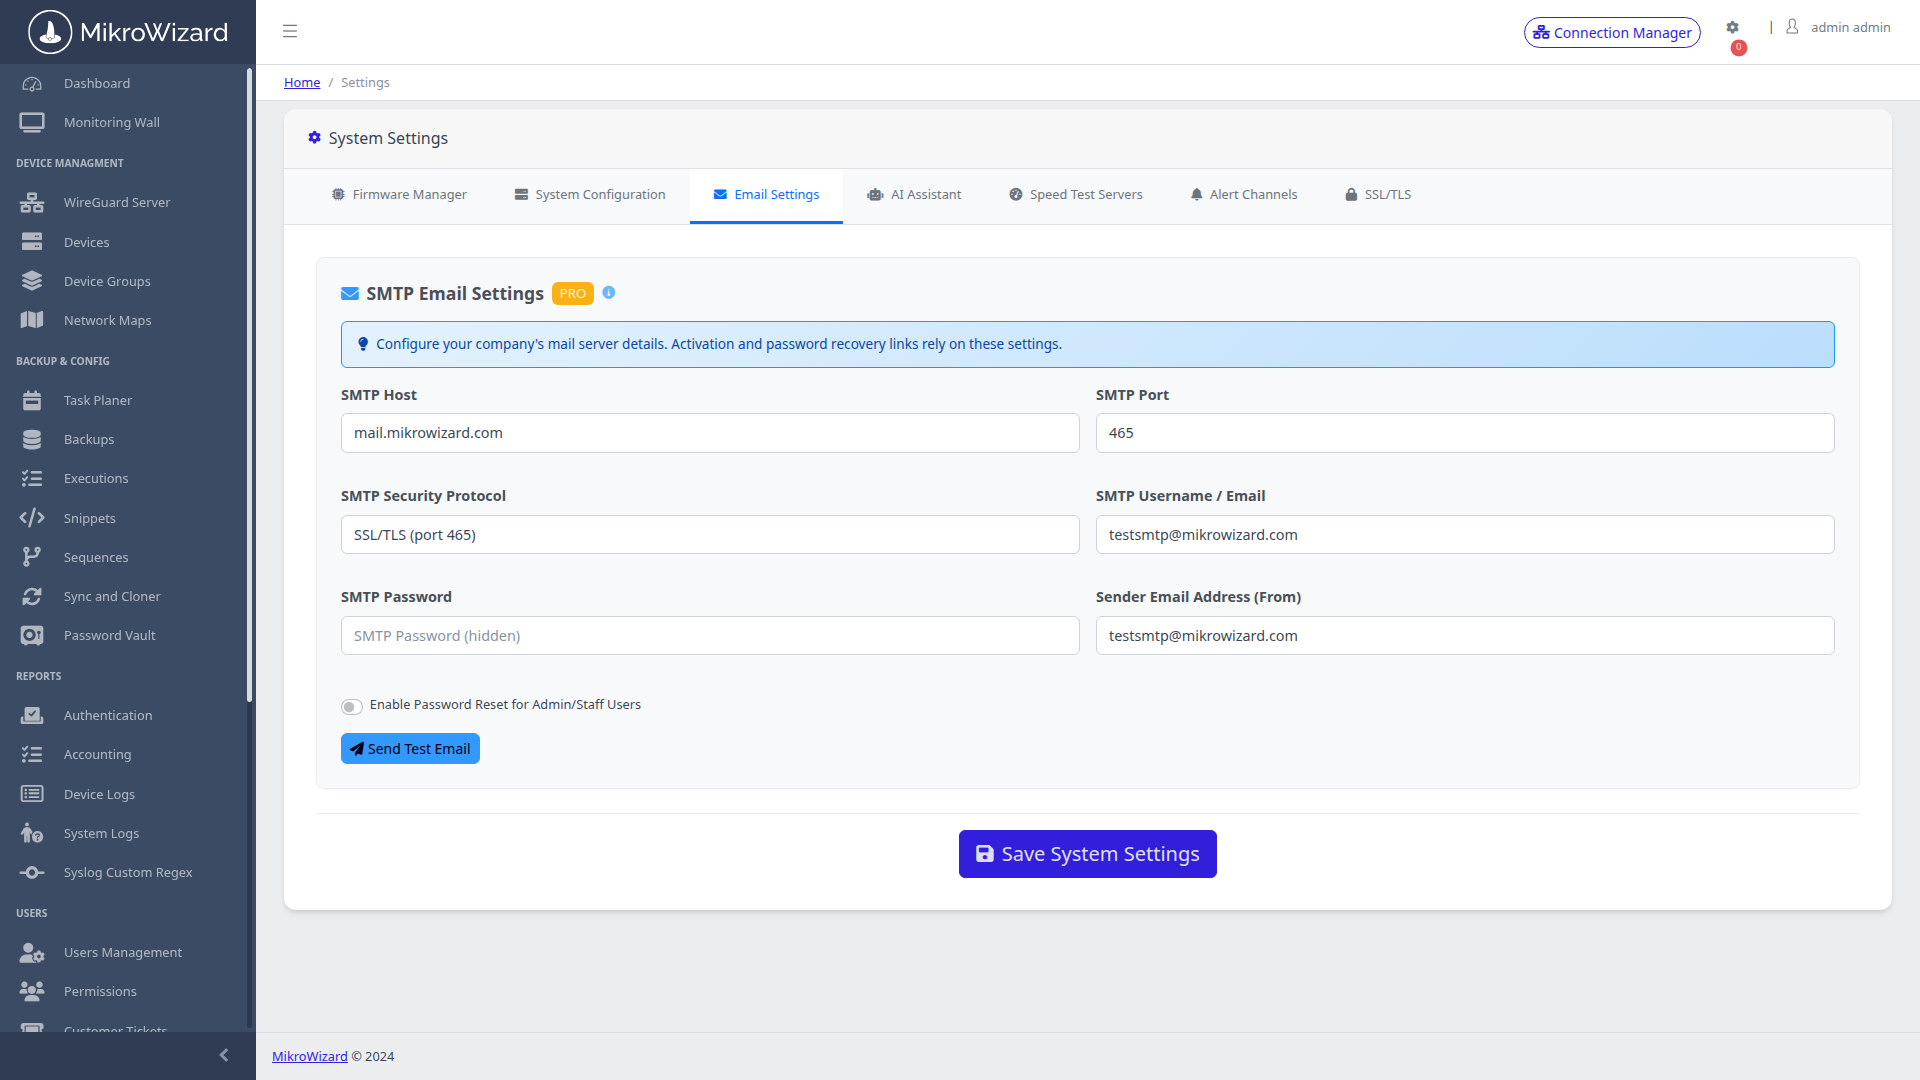
Reliable automated email delivery for critical network alerts, administrative password recovery, and audit report distribution via configurable SMTP relay.
Deploy on-premises. Maintain 5-tier forensic logs, regex syslog classifiers, and AI auditability.
 MikroWizard