Pillar 1 • Remote Access & Privileged Access Management

Zero-Trust Remote Access &
Privileged Access Management (PAM)

Secure remote access without open management ports, shared credentials, or unrecorded sessions. MikroWizard PAM covers SSH, Telnet, RDP, VNC, WebBox and WebFig in the browser, for MikroTik and for any other servers or network devices. Enforce remote Winbox 2FA via a built-in RADIUS server, kernel-level command blocking, session DLP policies, and recording for every protocol.

New in v2.1.0: browser RDP & VNC, WebBox (WinBox in the browser) and session DLP (Pro). Read the release notes →

Access

Zero-Client In-Browser HTML5 Terminal Gateway

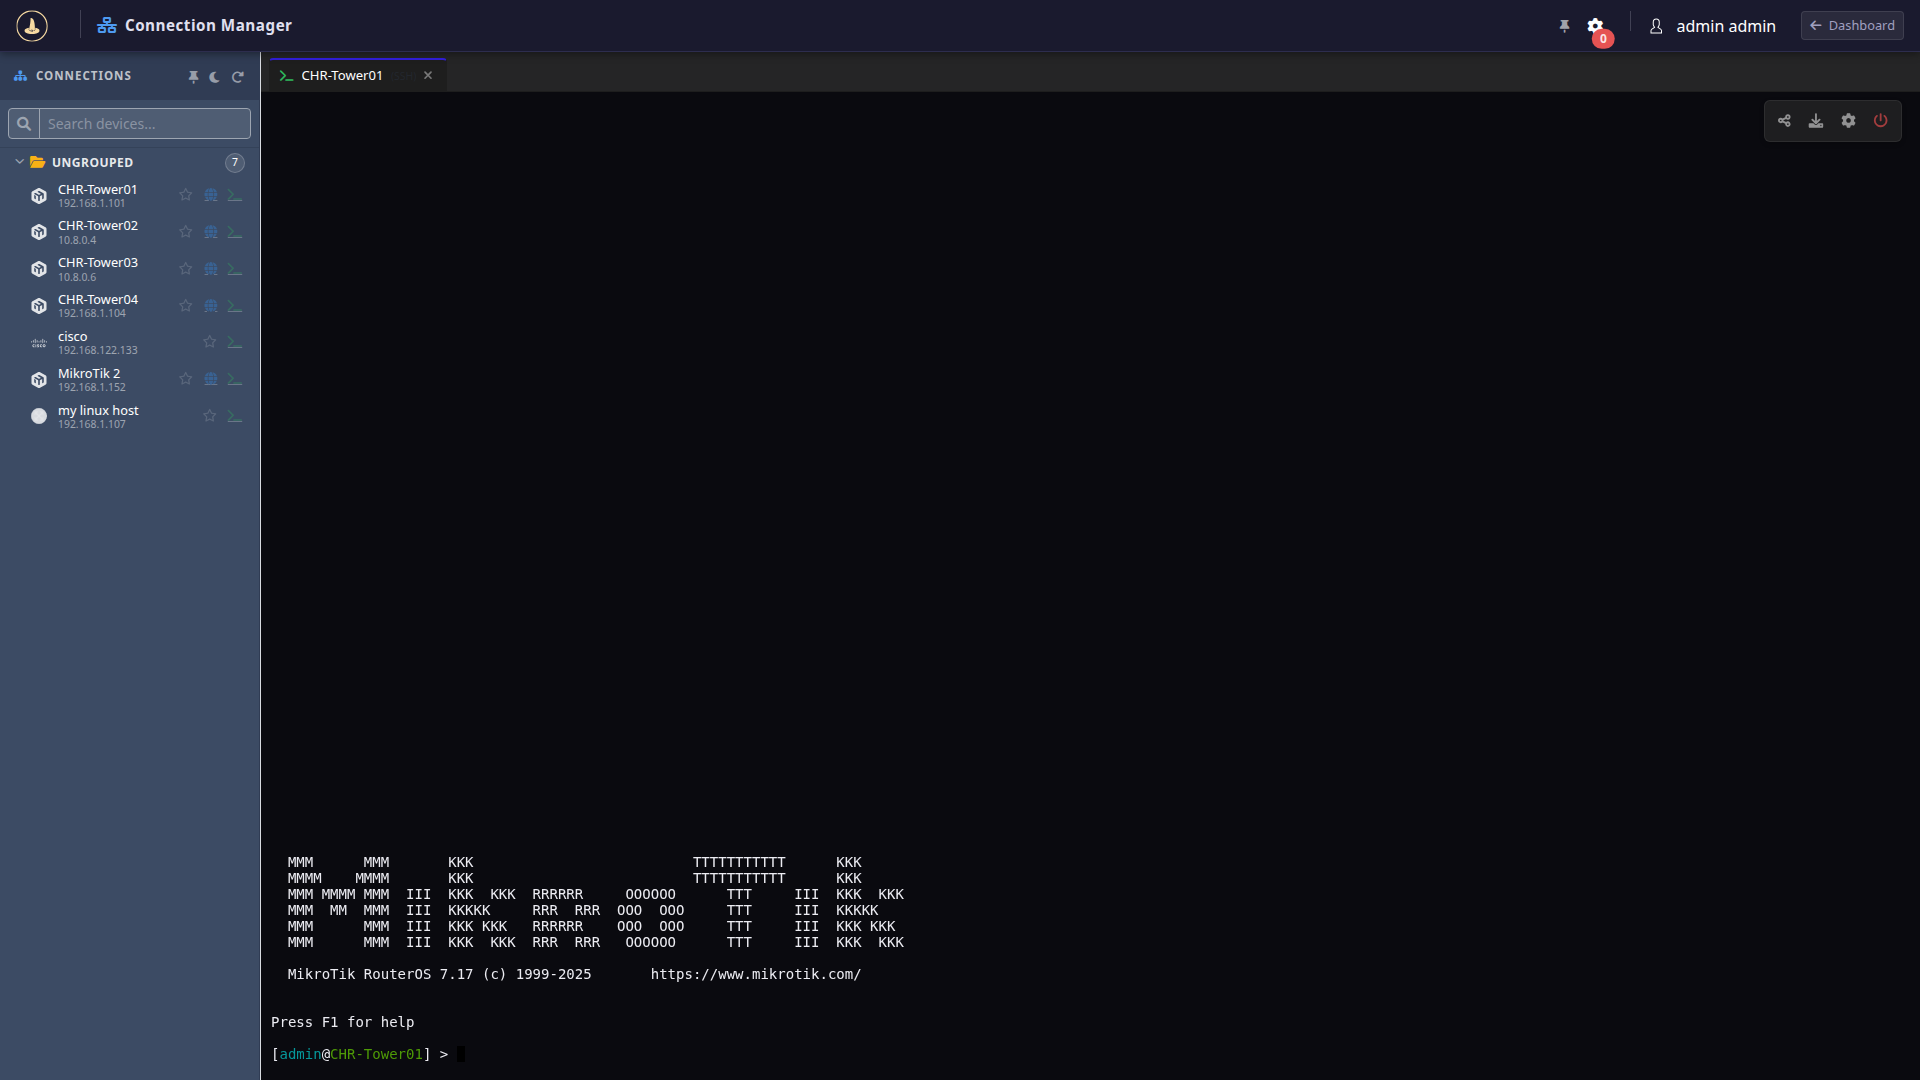
Engineers open terminal sessions directly in their browser powered by xterm.js over WebSockets. Router passwords are envelope-encrypted in the vault and injected into sessions automatically without user exposure.
  • ✓ Zero local SSH client software or VPN client installations required.
  • ✓ No exposed router management ports (port 22 or 23) needed on the public internet.
  • ✓ Multi-tab terminal switching across distributed core routers.
In-Browser Zero-Client Terminal Gateway
Inspect High-Res Screen

Interactive Terminal Session: Live WebSockets CLI connected to MikroTik CHR-Tower01 rendering active RouterOS prompt.

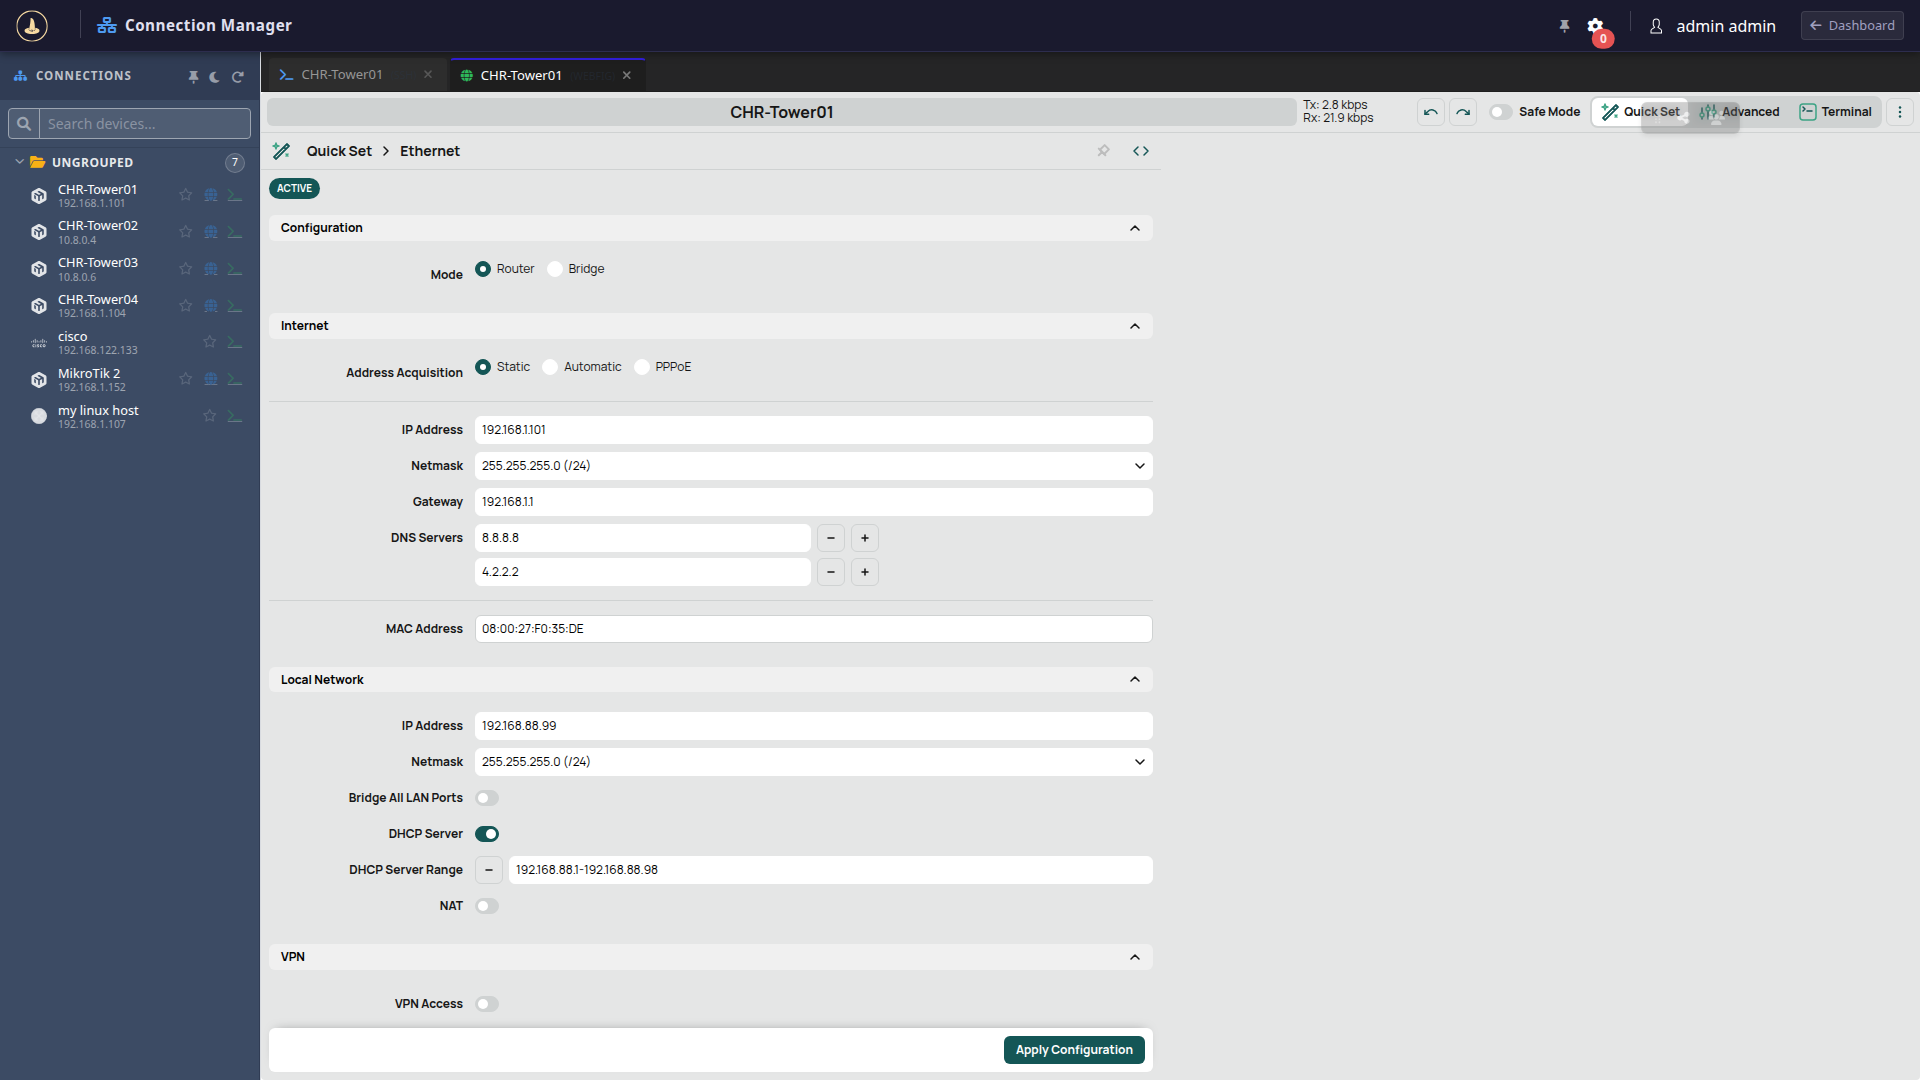
Reverse WebFig Proxy Interface
Inspect High-Res Screen

Multiplexed WebFig GUI: Embedded RouterOS WebFig GUI proxied through secure backend tunnels without public IPs.

GUI Proxy

Secure WebFig Reverse Proxy (Zero Port Exposure)

Access the full graphical MikroTik WebFig interface for any router in your fleet without configuring firewall NAT port forwardings or assigning static public IPs to edge devices.

  • ✓ Multiplexes HTTP/WebSocket WebFig traffic through the central MikroWizard engine.
  • ✓ Protects routers behind CGNAT and dynamic cellular uplinks.
New in v2.1 • Pro • Any Windows/Linux host

Clientless RDP & VNC in the Browser

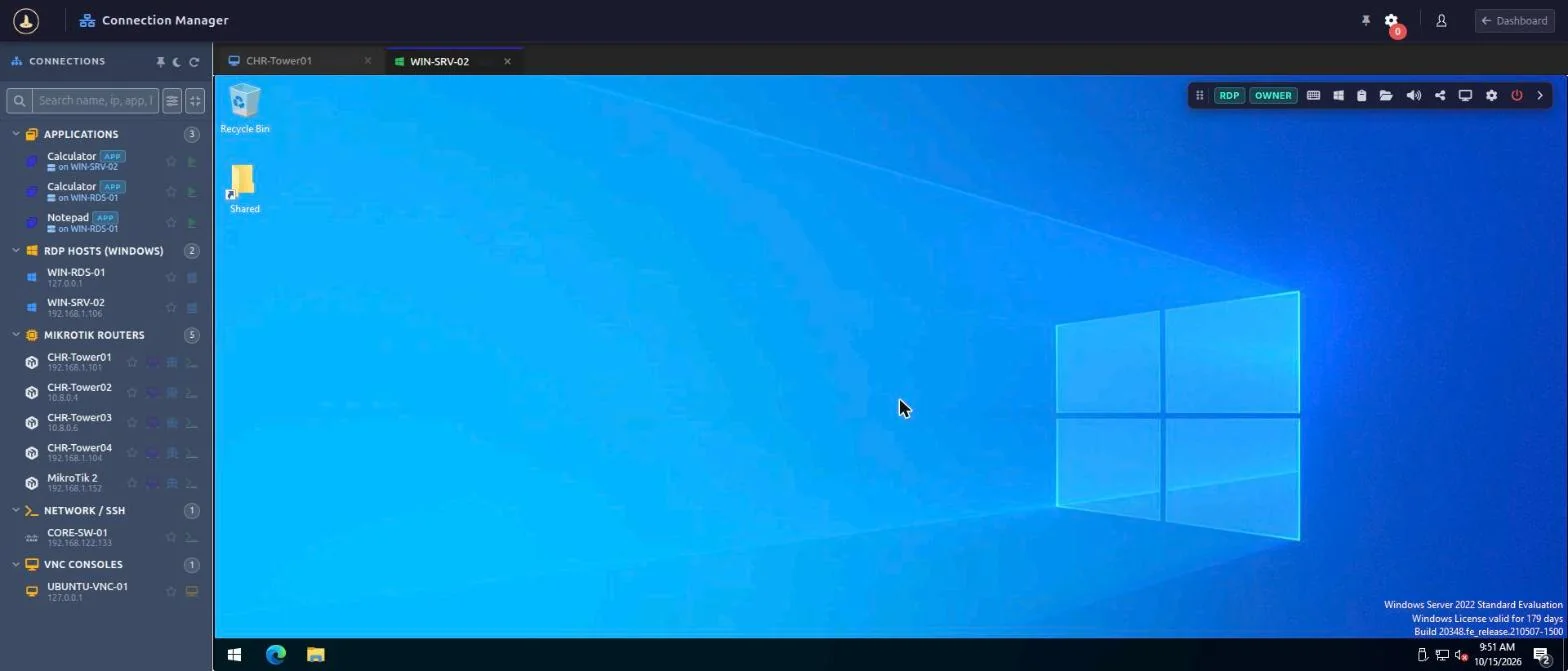
Open RDP and VNC desktop sessions from the Connection Manager, right next to SSH, Telnet and WebFig. Sessions run as HTML5 in the browser, so operators install nothing. RDP and VNC work with any Windows or Linux host; they are not limited to MikroTik.
  • ✓ Browser RDP and VNC in the browser with no desktop client on the operator's machine.
  • ✓ Recorded and replayable in the browser, and can be watched or shared live like terminal sessions.
  • ✓ Requires the Terminal Gateway addon (v1.3.0).
  • → Learn more about browser RDP & VNC
Clientless browser RDP session to a Windows Server in MikroWizard PAM
Inspect High-Res Screen

Browser RDP Session: Windows Server desktop opened from the Connection Manager, no client installed.

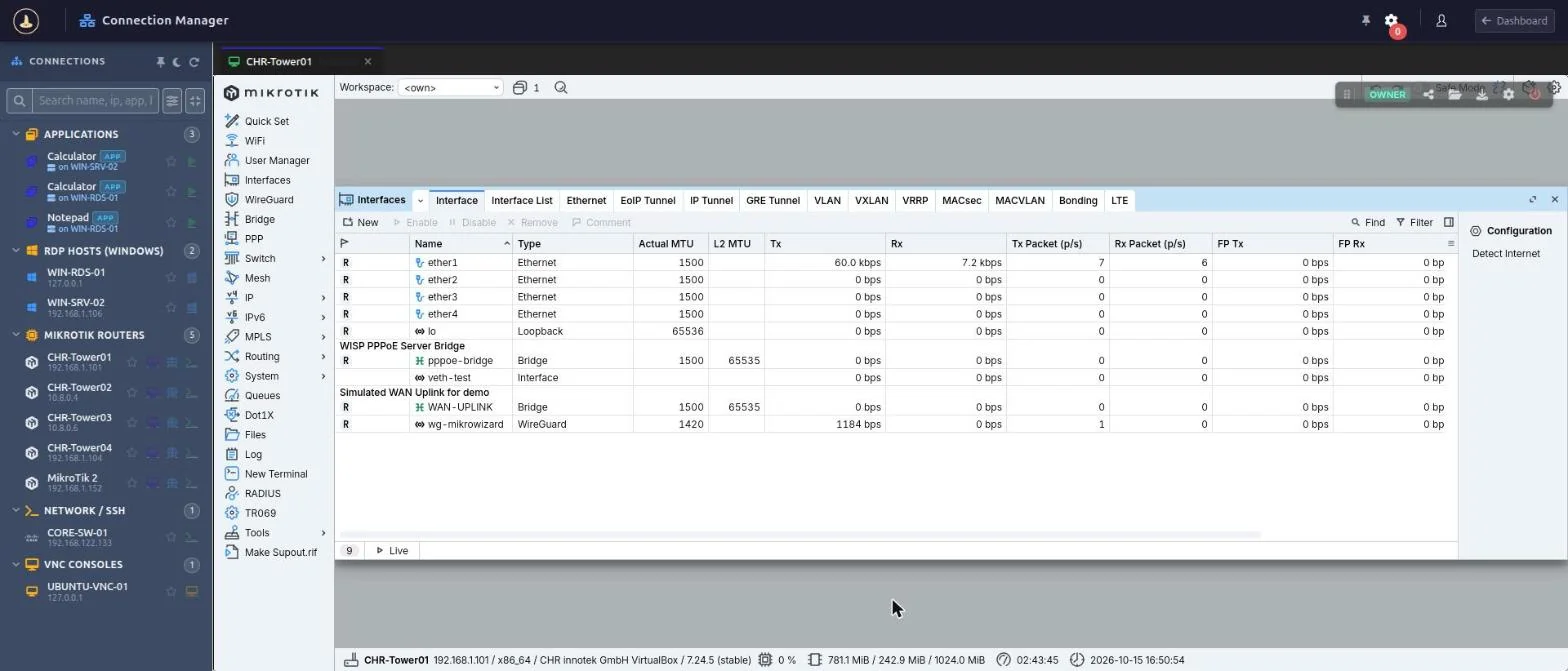
WebBox running WinBox 4 in the browser inside the MikroWizard Connection Manager
Inspect High-Res Screen

WebBox Session: WinBox 4 streamed to the browser from an isolated sandbox on the gateway.

New in v2.1 • Pro • MikroTik

WebBox: Remote WinBox in the Browser

WebBox is web WinBox for MikroTik devices. The gateway runs MikroTik's WinBox 4 for Linux in an isolated sandbox and streams it to the browser, so operators need no local WinBox install and the WinBox port is never exposed to them.

  • ✓ Launch from the Connection Manager, device list, device tree or Network Map, with a gateway availability check.
  • ✓ Each session gets an isolated temporary drive.
  • ✓ Recorded as MP4 with seeking, and can be watched or shared live.
New in v2.1 • Pro

RemoteApp Publishing & Protocol Templates

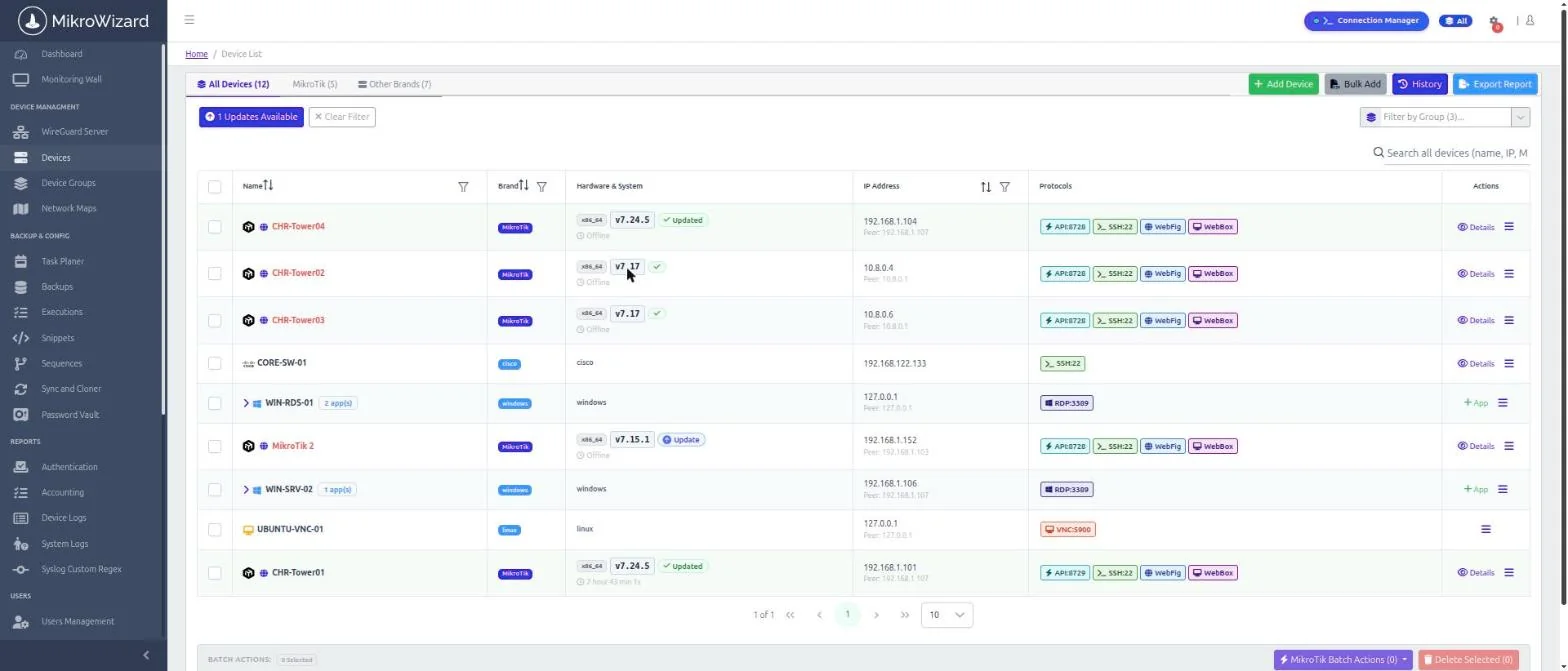
Publish single applications from an RDP host as child entries nested under the server; they inherit its IP. Separate CLI, RDP and VNC templates carry display and acceleration settings.
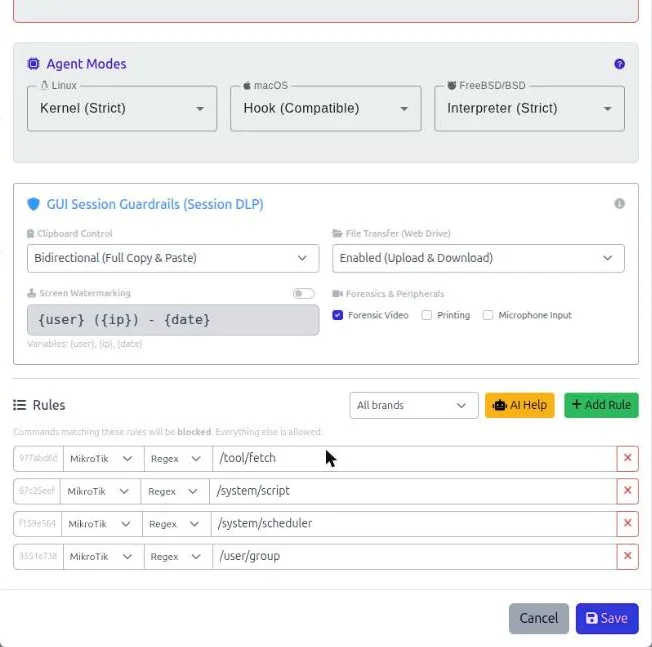
  • ✓ Four-tier session options: template → host → published app → DLP policy.
  • ✓ One inventory for MikroTik, Cisco, Windows and Linux, with protocol badges per device.
Device list with MikroTik, Cisco, Windows and Linux devices and API, SSH, WebFig, WebBox, RDP and VNC badges
Inspect High-Res Screen

Multi-Protocol Inventory: MikroTik, Cisco, Windows and Linux devices with their available access protocols.

PAM policy with session DLP settings for clipboard, file transfer, watermark and forensic recording
Inspect High-Res Screen

Session DLP Policy: Clipboard, file transfer, watermark and forensic video settings per policy.

New in v2.1 • Pro

Session DLP Policies

Control what can leave a privileged session. Each policy decides clipboard access, file transfer, watermarking and forensic recording for the sessions it applies to.

  • ✓ Clipboard and file transfer rules per policy.
  • ✓ Watermarking and forensic recording for accountability.
Policy Enforcement

Kernel-Level System Call Command Interception

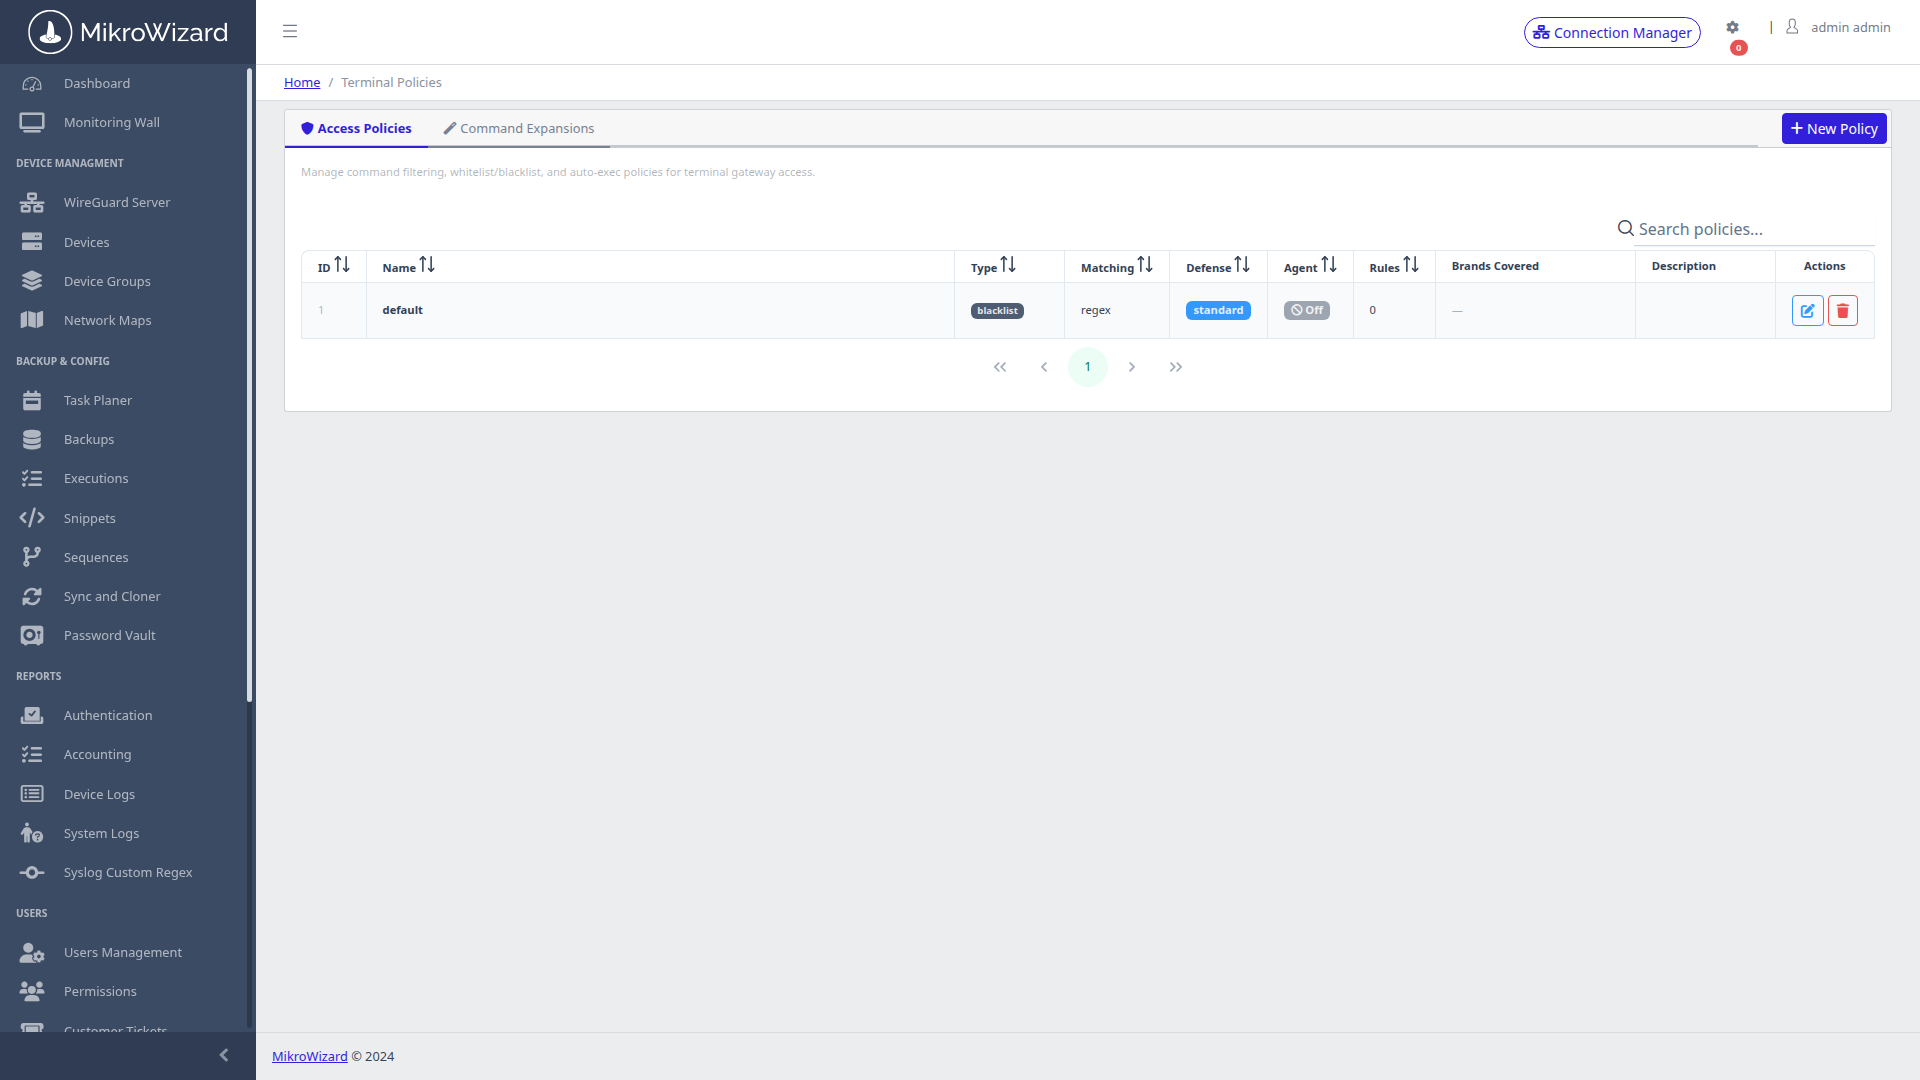
Prevent catastrophic operational accidents before they happen. Terminal sessions pass through a Linux daemon instrumented with ptrace system-call tracing that evaluates keystroke buffers against active regex policies.

  • ✕ Instantly blocks destructive commands like rm -rf / or unauthorized reboots.
  • ✓ Granular regex matchers with custom warning alerts and audit alerts.
Security Policies List
Inspect High-Res Screen

Security Policy Engine: Rule definitions specifying allowed and blocked command patterns across fleet groups.

Live Session Sharing Modal
Inspect High-Res Screen

Multi-Operator Sharing: Generate guest invitation tokens with granular Owner, Collaborator, and Read-Only Observer roles.

Collaboration

Real-Time Terminal Collaboration Rooms

Troubleshoot complex network incidents together. Multiple engineers can connect to the same live CLI terminal simultaneously with defined role-based interaction permissions.

  • ✓ Owner Role: Initiates session, controls invite permissions, and retains killswitch authority.
  • ✓ Collaborator Role: Interactive write access for pair troubleshooting.
  • ✓ Observer Role: View-only access for training, auditing, and junior shadow sessions.
Audit Forensics

Asciinema Keystroke Recording & Web Player

Every character typed and every output byte rendered during terminal sessions is captured in lightweight, tamper-evident Asciinema v2 format (.cast).
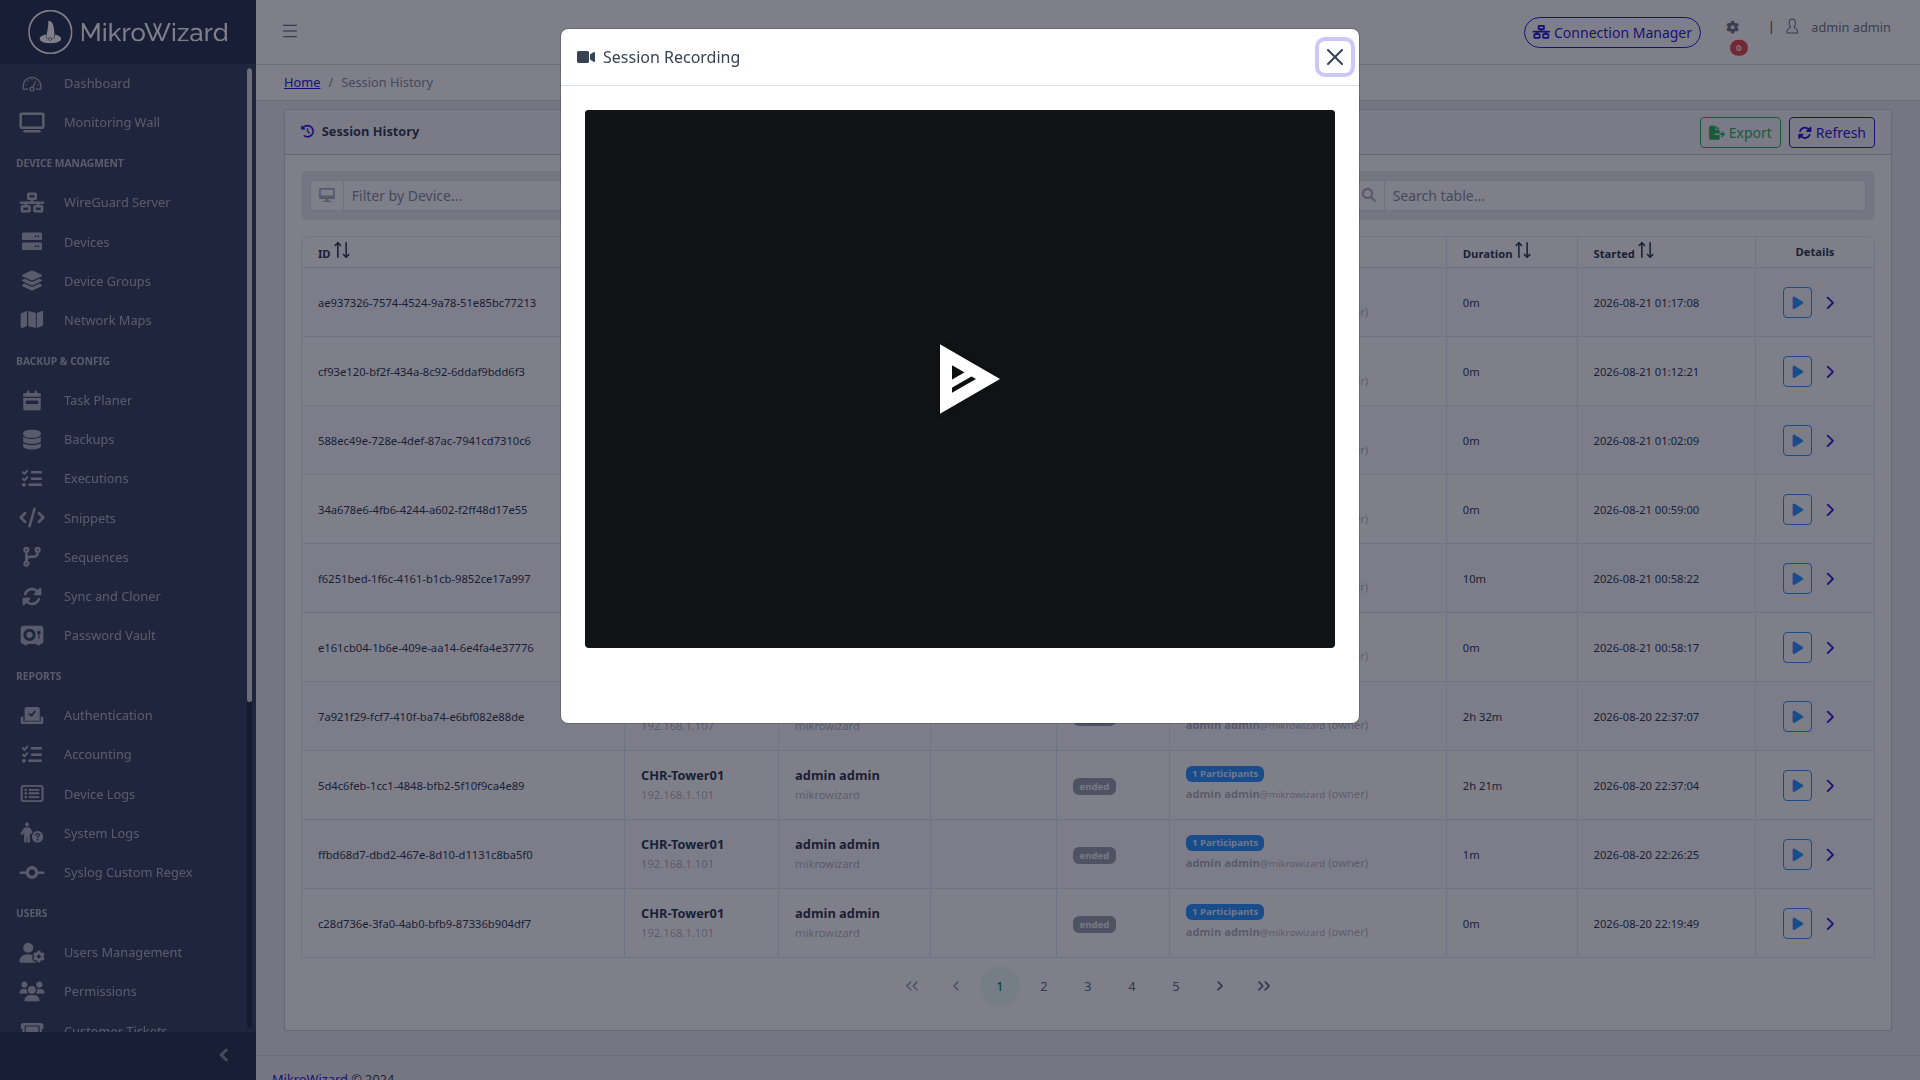
  • ✓ In-browser interactive player with timeline scrubber, play/pause, and adjustable playback speed.
  • ✓ High compression ratio: hours of session history stored in mere kilobytes instead of gigabytes of heavy video.
Asciinema Session Playback Player
Inspect High-Res Screen

Session Forensics Player: Scrubbable playback modal rendering precise terminal state reconstruction.

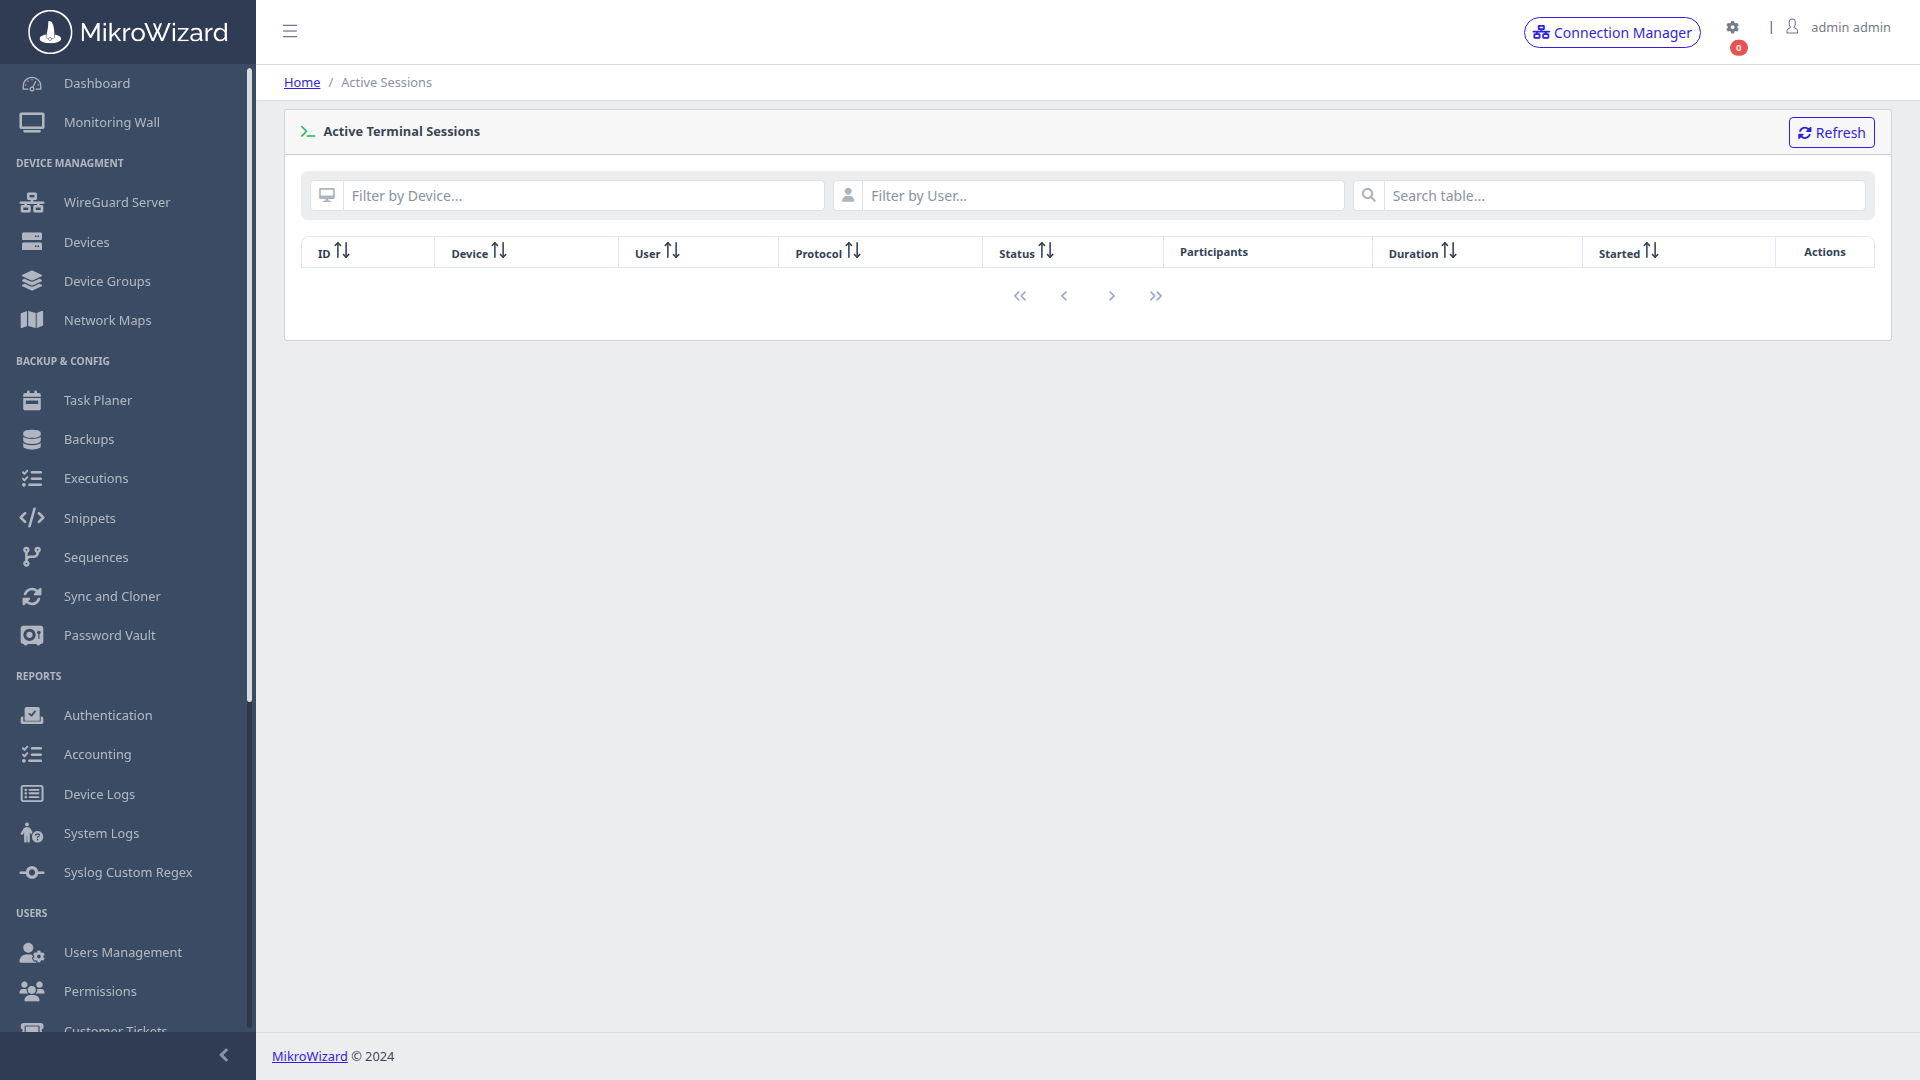
Active PAM Sessions Console
Inspect High-Res Screen

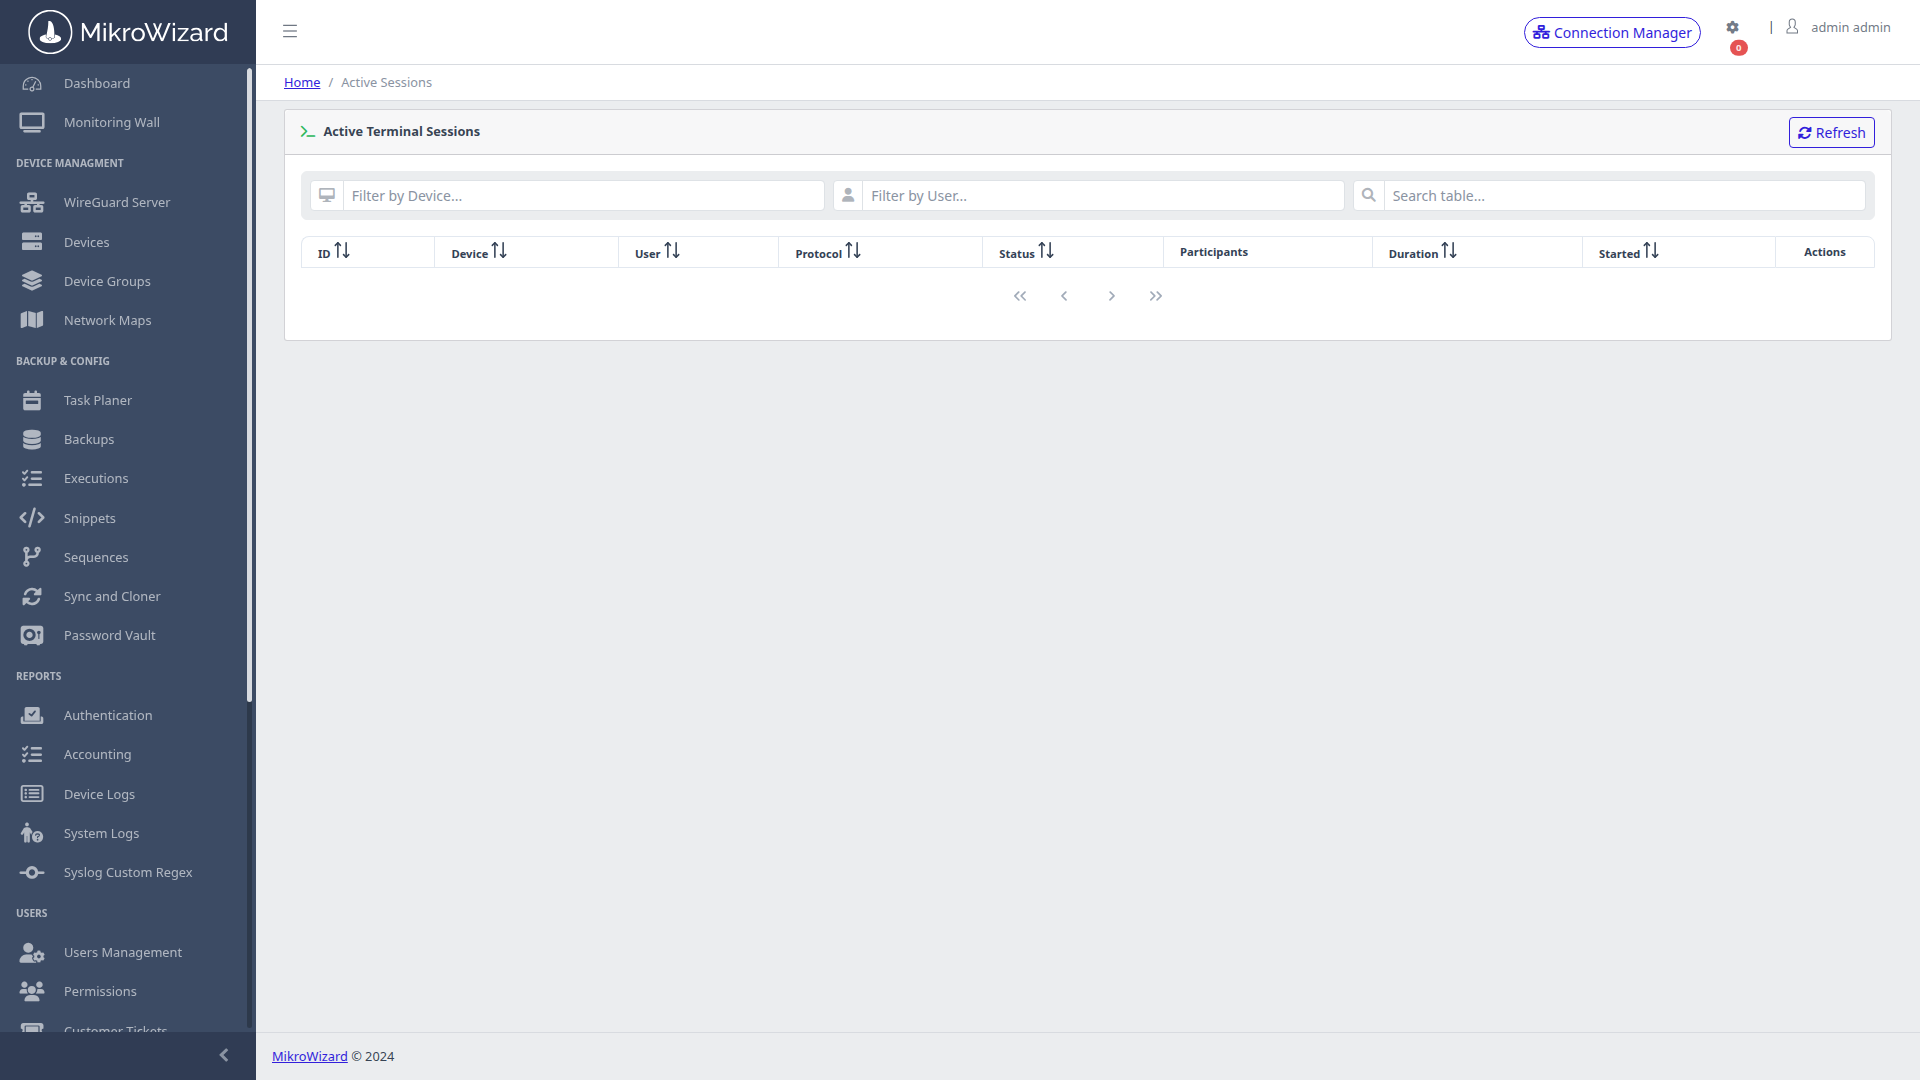
Active Session Dashboard: Real-time table of all active connections with operator IP, duration, and 1-click termination.

Oversight

Active PAM Console & 1-Click Killswitch

Security directors and NOC supervisors maintain live visibility over all active terminal sessions across the entire organization.

  • ✓ See connected operator name, target router IP, protocol, and session duration.
  • ✕ Instantly terminate suspicious or rogue sessions with 1 click using the emergency killswitch.
Winbox 2FA

Native Winbox & SSH 2FA via Built-in RADIUS Server

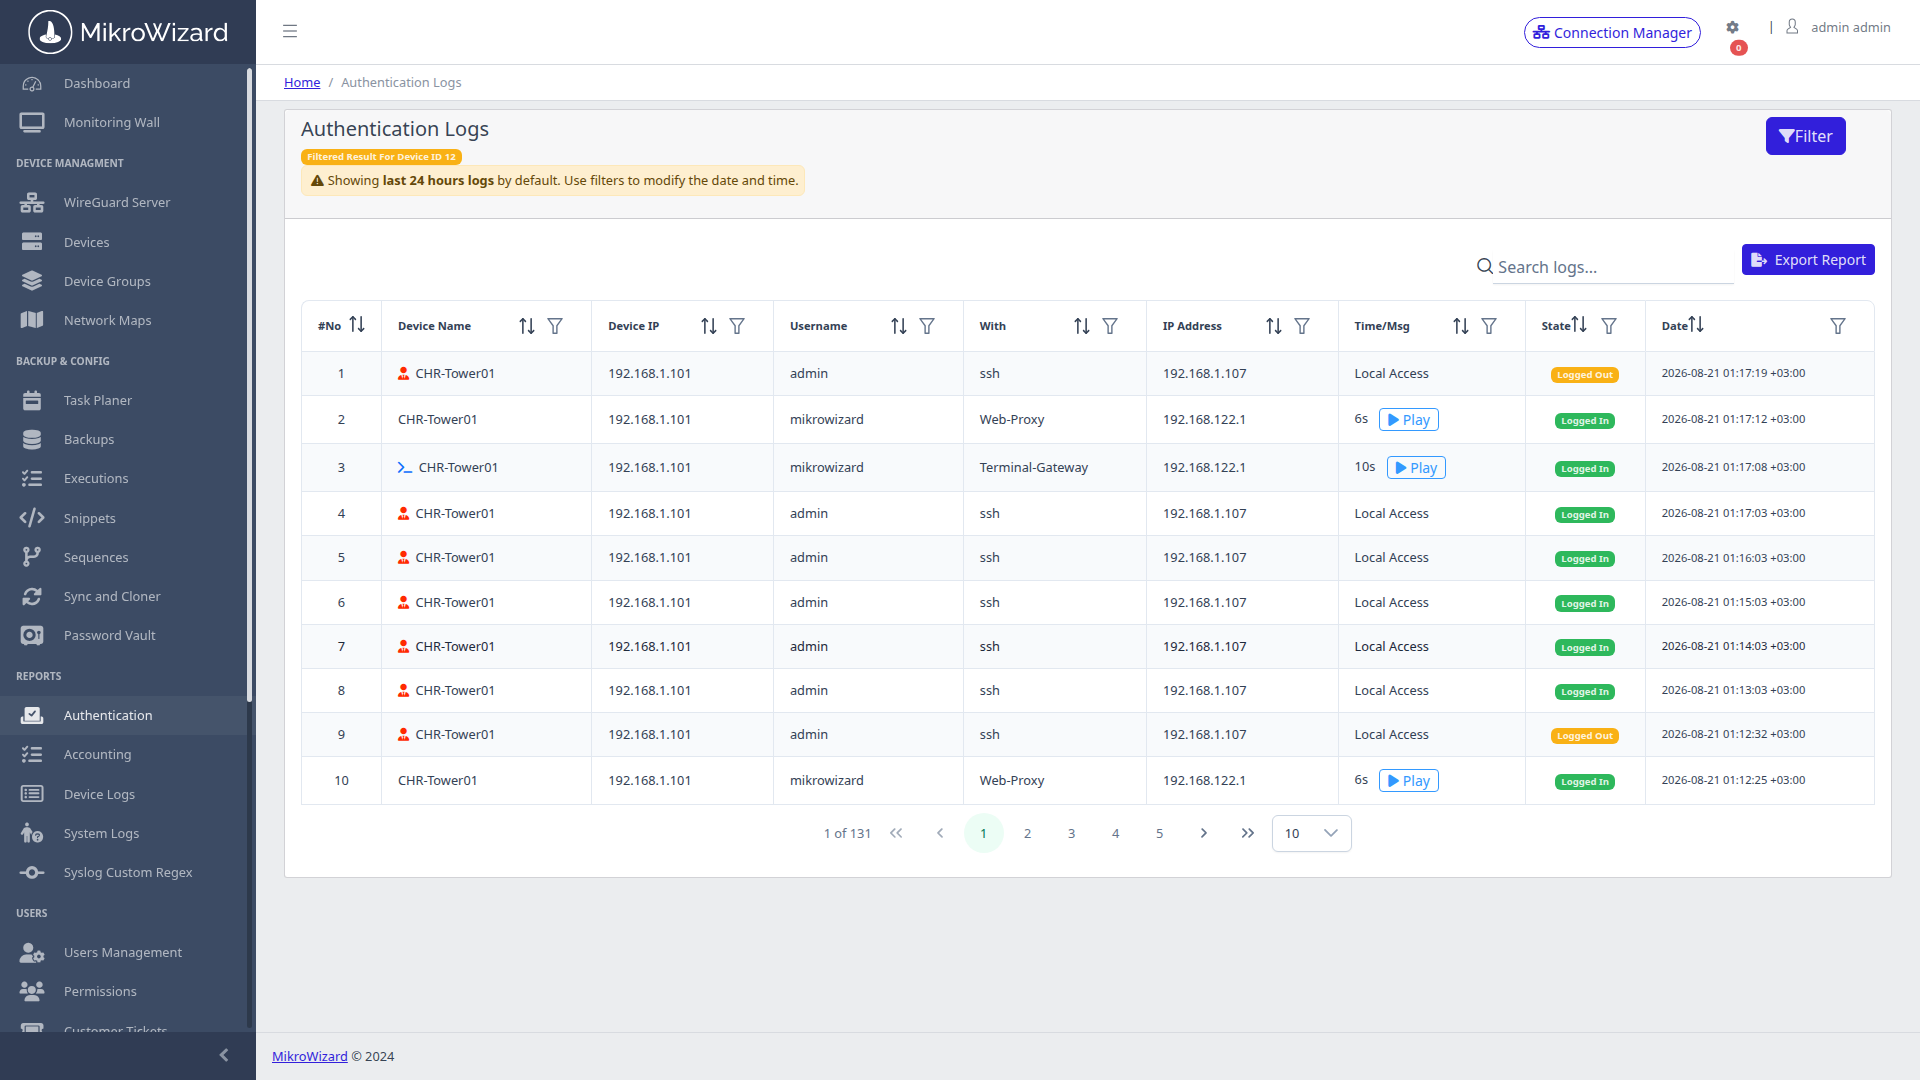
RouterOS natively lacks built-in dynamic Two-Factor Authentication. MikroWizard solves this with a built-in RADIUS server listening on standard RADIUS authentication ports.

  • ✓ When logging in via desktop Winbox, enter Password+TOTP (e.g. MySecret123456).
  • ✓ The RADIUS server intercepts the MS-CHAPv2 payload, validates credentials, and confirms the 6-digit TOTP token.
RADIUS Authentication Log
Inspect High-Res Screen

RADIUS Authentication Log: Report of login attempts handled by the built-in RADIUS server for 2FA-protected Winbox and SSH access.

Password Vault Policy Settings
Inspect High-Res Screen

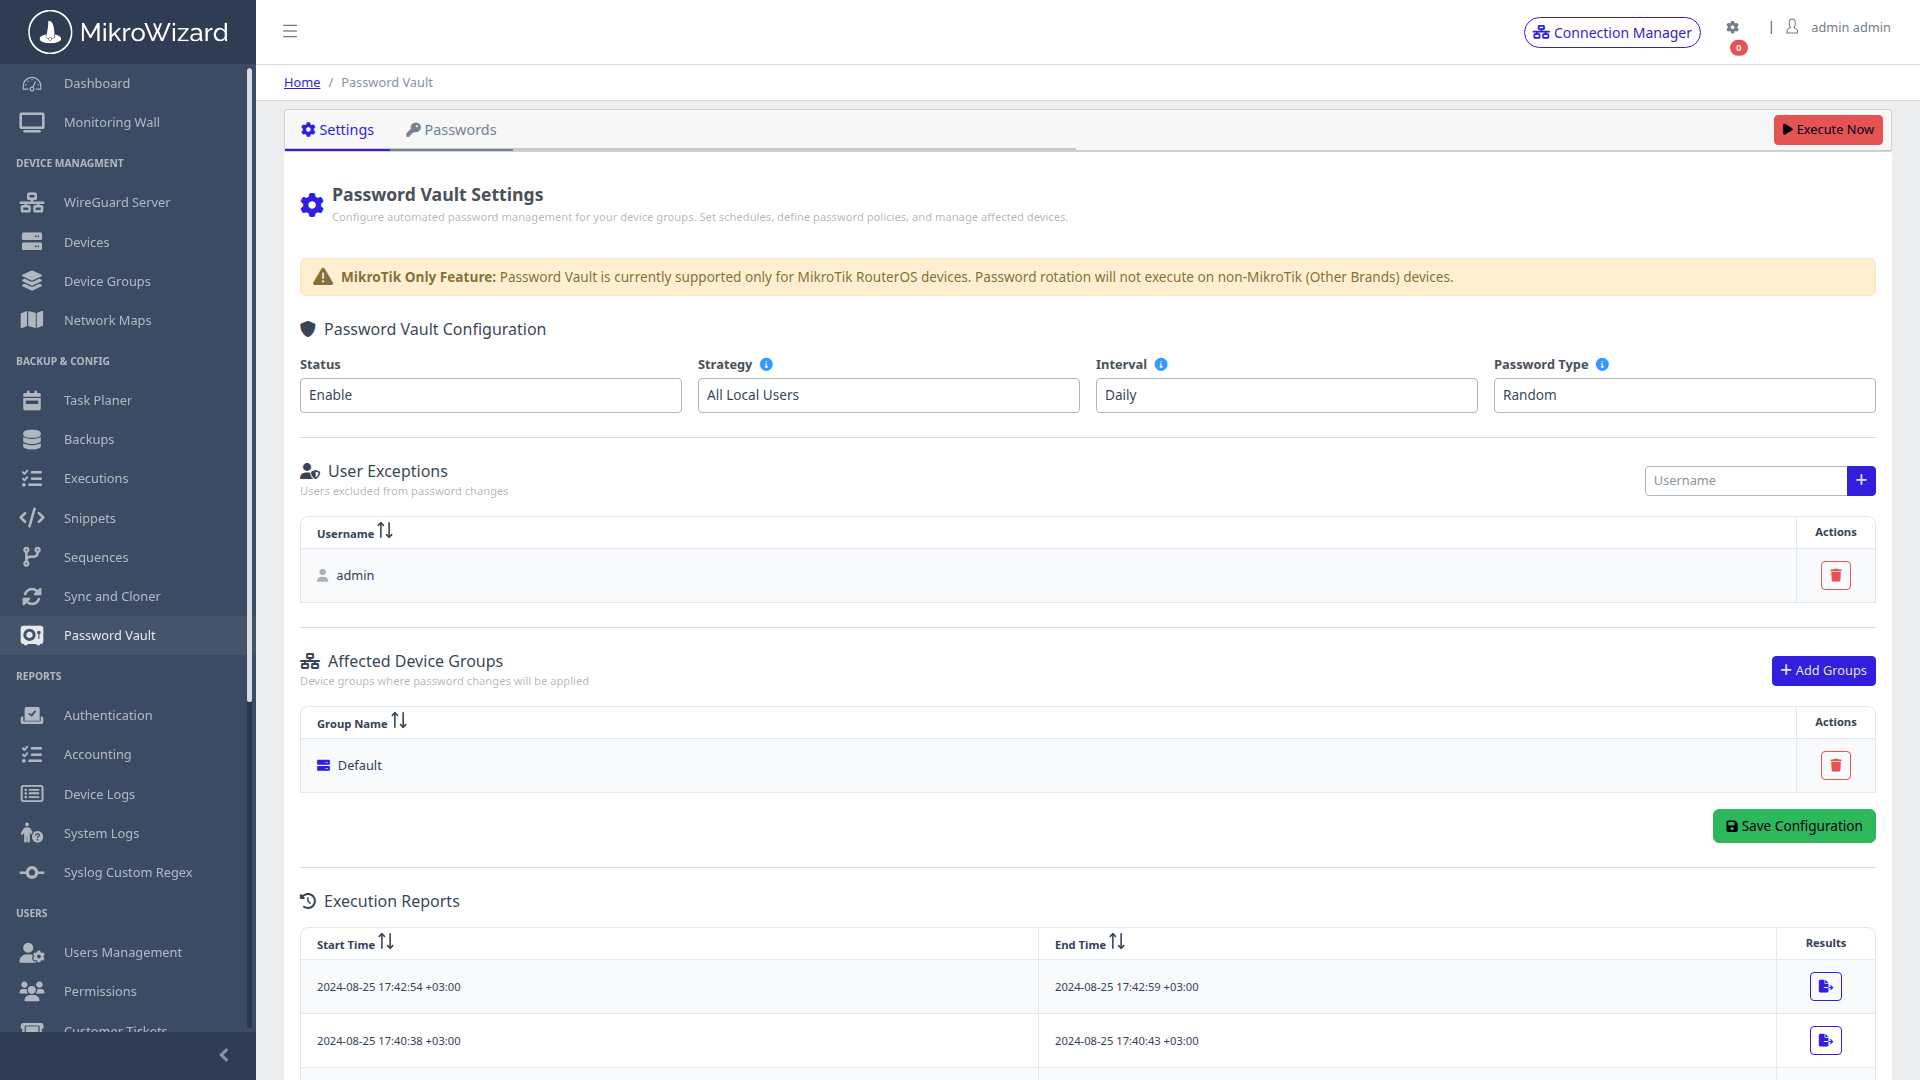
Encrypted Credential Vault: Automated password rotation rules and complexity policies across device tiers.

Credential Vault

Encrypted Password Vault & Automated Rotation

Stop storing router administrative passwords in unencrypted spreadsheets. The integrated vault secures all access credentials with envelope encryption: each credential gets its own data key, wrapped by a master key.

  • ✓ Automated scheduled credential rotation across thousands of routers simultaneously.
  • ✓ Zero-knowledge credential injection: operators access routers without knowing the raw root password.
Multi-Vendor

Multi-Vendor CLI Terminal Protocol Templates

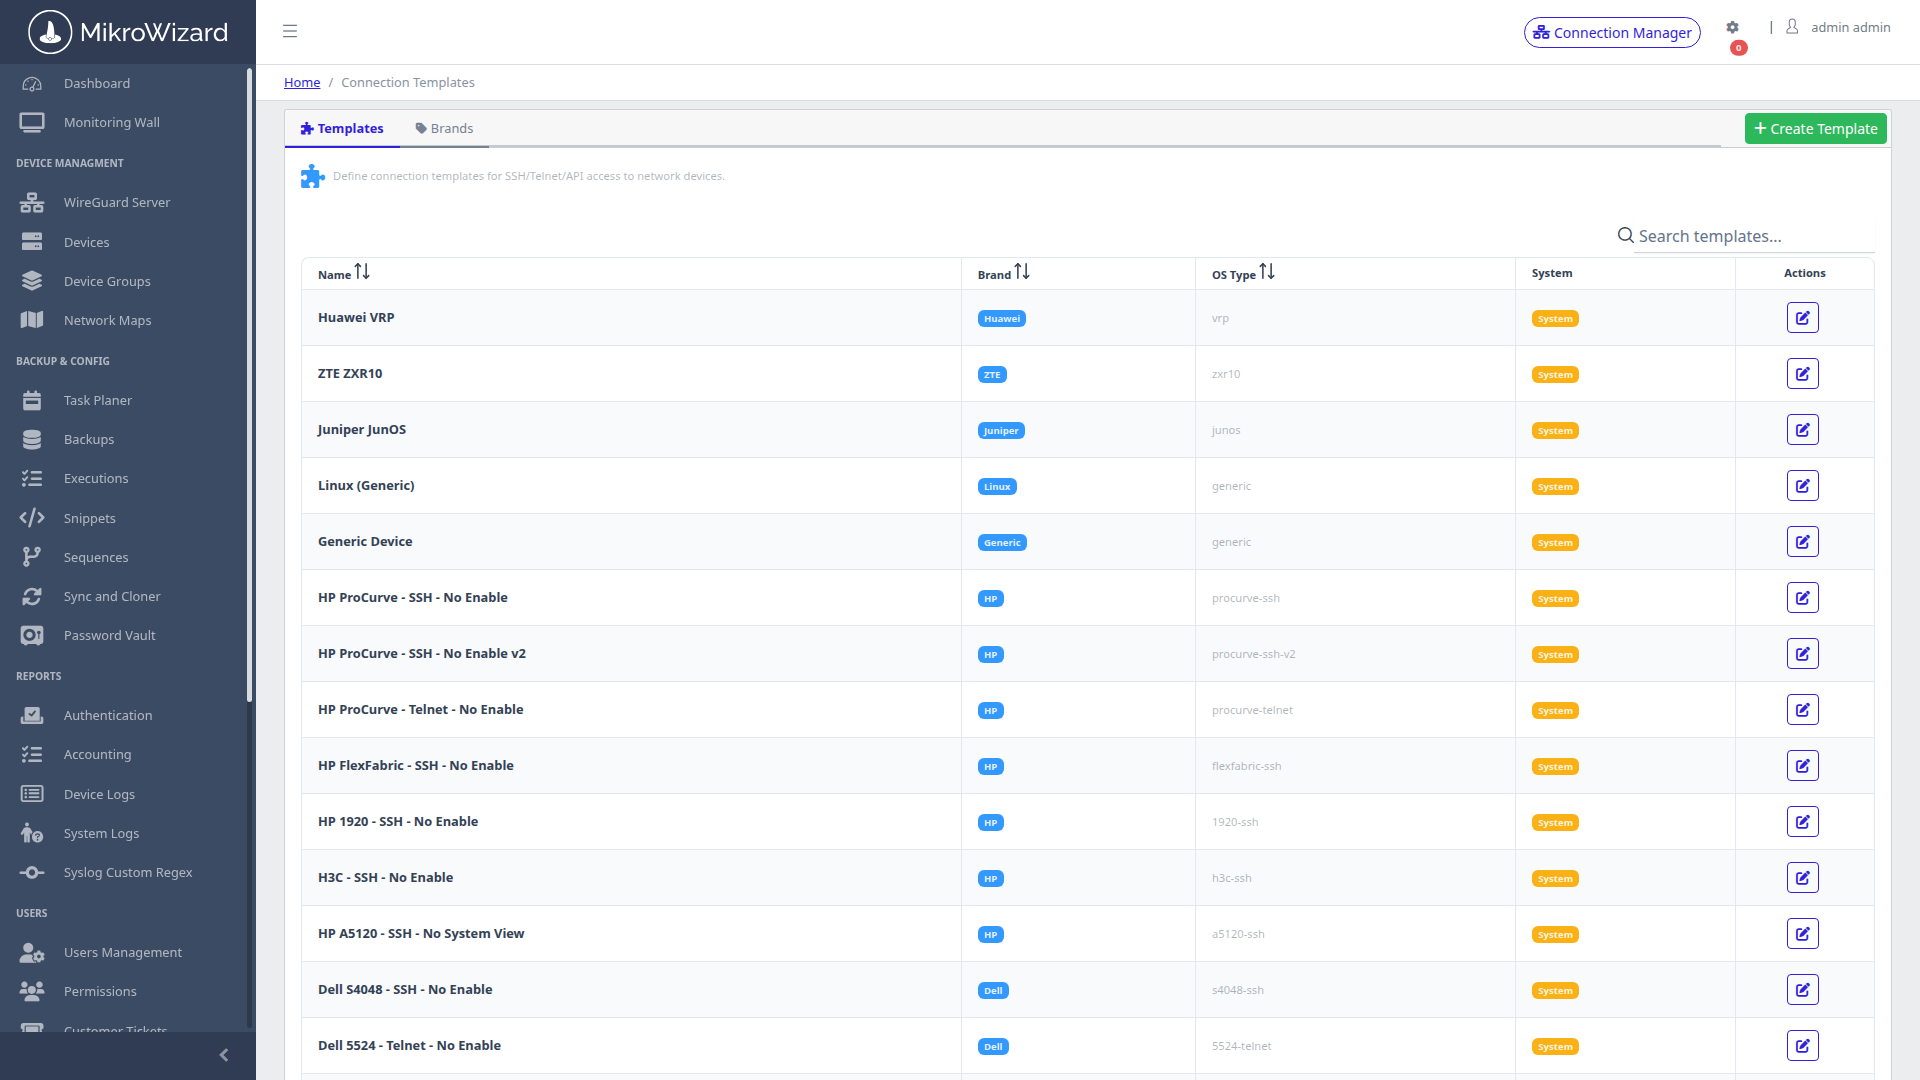
PAM is not limited to MikroTik RouterOS: MikroWizard's terminal engine includes dynamic protocol templates for Cisco IOS, Linux bash, VyOS, and EdgeOS.
  • ✓ Configurable prompt matchers, escape sequences, and line termination settings.
  • ✓ Unified terminal gateway experience across heterogeneous datacenter equipment.
CLI Terminal Protocol Templates Library
Inspect High-Res Screen

Protocol Template Directory: Pre-configured and custom prompt definitions for heterogeneous network devices.

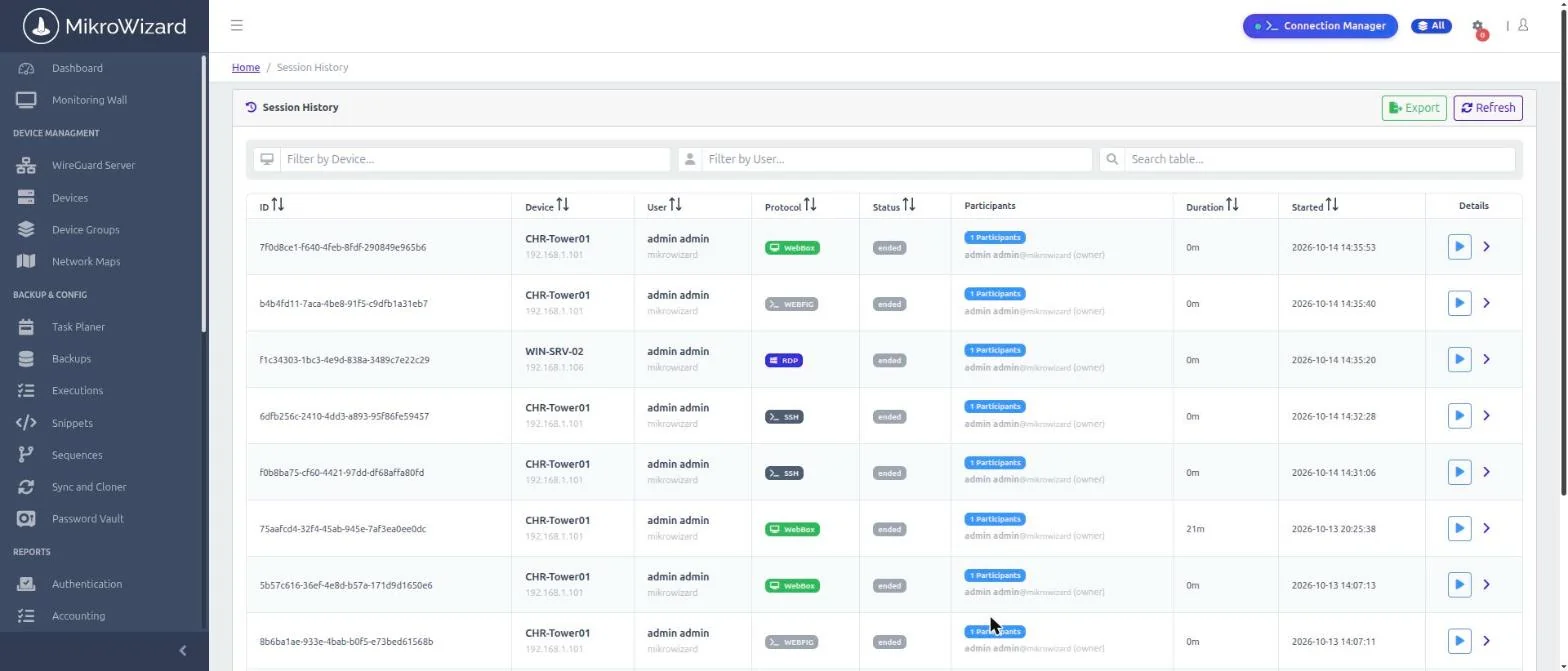
PAM session history with recordings for SSH, RDP, VNC, WebBox and WebFig sessions
Inspect High-Res Screen

Session History: Recordings for every protocol, replayable in the browser.

New in v2.1 • Pro

Recording & Live Sharing for Every Protocol

Every protocol is recorded and replayable in the browser: RDP and VNC replay in the browser, WebBox as MP4. Ended WebFig proxy sessions appear in session history too.

  • ✓ RDP, VNC and WebBox sessions can be watched or shared live, like terminal sessions.
  • ✓ Protocol badges in the Session Manager for SSH, RDP, VNC, WebBox and WebFig.
  • ✓ Join and guest links are bound to the signed-in user to prevent spoofing.
Zero-Trust Ready

Secure Your Network Fleet with MikroWizard PAM

Deploy on-premises with Docker: one installer script deploys the core and all containers in about 5 minutes on a good connection. Experience zero-client terminal access, kernel policy enforcement, and live collaboration.
Request Live Architecture Demo Explore Pricing Plans