Pillar 5 • Auditing, Compliance & AI

5-Tier Centralised Audit Trails &
Deterministic Network AI Copilot

Helps you collect audit evidence for ISO 27001, SOC 2 and PCI-DSS. Centralize RADIUS, Syslog, CLI commands, and Apprise multi-channel alerts, backed by an AI Copilot with complete tool execution auditability.

Compliance

Centralized 5-Tier Audit Log Suite

Unifies 5 distinct forensic logging layers into a single centralised, searchable audit repository:
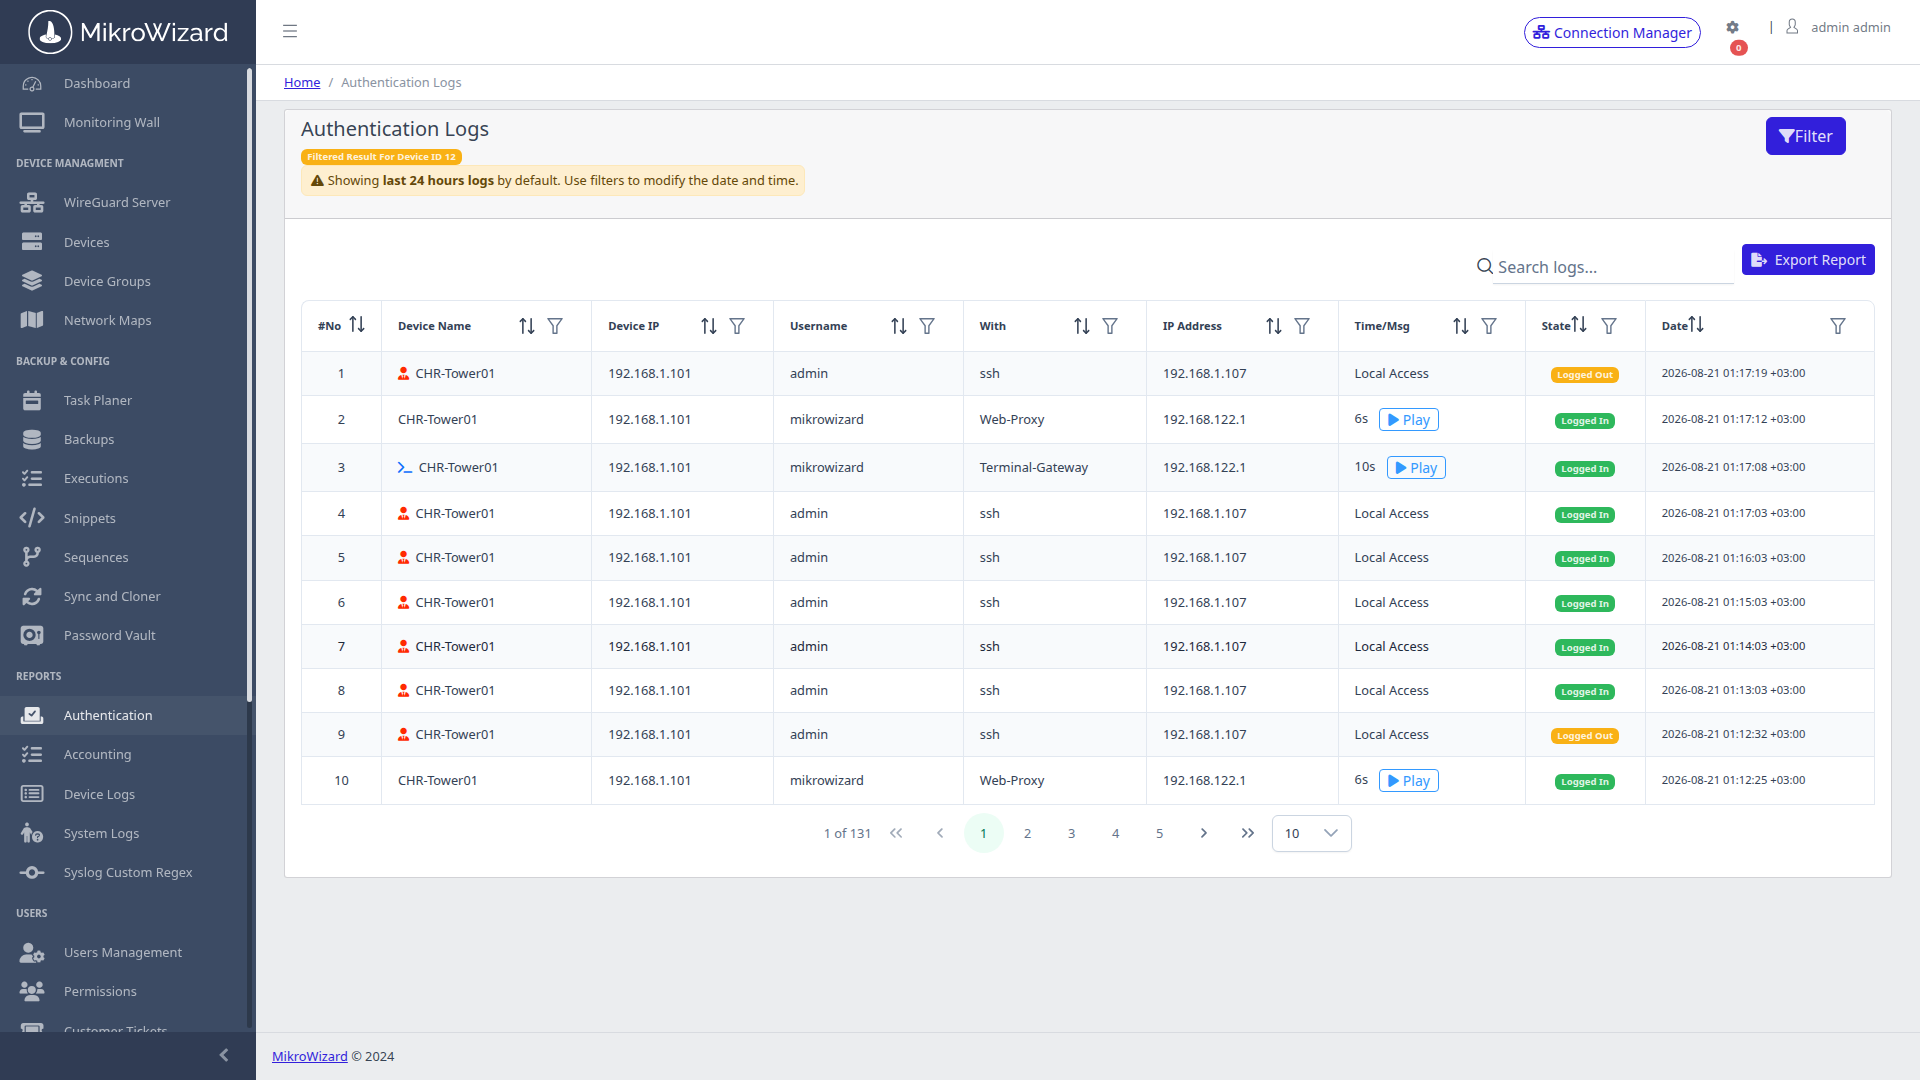
  • 1. RADIUS Auth Logs : Every login attempt, client IP, NAS-IP, and Accept/Reject reason.
  • 2. RADIUS Accounting : Session duration, octets in/out, and disconnect cause.
  • 3. CLI Command Audit : Time-stamped keystrokes and command lines executed per operator.
  • 4. Device Event Logs : Interface flaps, BGP neighbor state transitions, and hardware alerts.
  • 5. System Event Trail: User role alterations, vault access, and configuration restores.
RADIUS Authentication Audit Log
Inspect High-Res Screen

RADIUS Forensic Table: Detailed records of operator authentication, NAS identifier, and OTP token statuses.

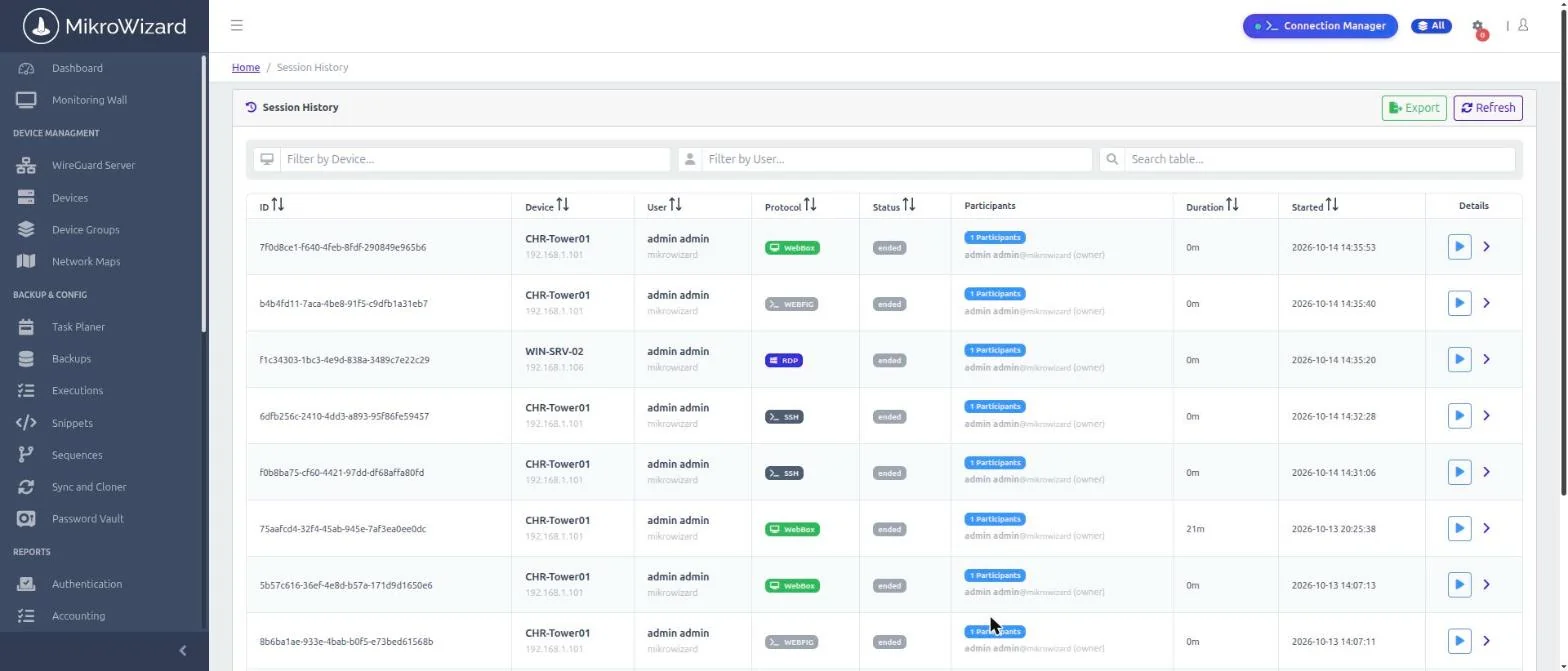
MikroWizard PAM session history listing SSH, RDP, VNC, WebBox and WebFig sessions with protocol badges and recordings
Inspect High-Res Screen

Session History: Every session with its protocol badge and a recording you can replay in the browser.

Session Audit PAM Pro

Session Audit for Every Protocol

Privileged access management (PAM) for network devices and servers needs one audit trail, whatever the protocol. Since MikroWizard 2.1.0, SSH, Telnet, RDP, VNC, WebBox and WebFig sessions are all recorded and can be replayed in the browser.

  • ✓ Browser replay: RDP and VNC sessions replay in the browser; WebBox (WinBox in the browser) sessions are recorded as MP4 with seeking.
  • ✓ WebFig included: ended WebFig proxy sessions appear in session history.
  • ✓ Protocol badges in Session Manager show at a glance how each operator connected.
  • ✓ Watch live: RDP, VNC and WebBox sessions can be watched or shared like terminal sessions; join and guest links are bound to the signed-in user.

RDP, VNC and WebBox need the Terminal Gateway addon (v1.3.0). RDP and VNC work with any Windows or Linux host; WebBox is for MikroTik devices. Read the 2.1.0 release post →

Session DLP PAM Pro

DLP Watermarking & Forensic Recording per Policy

Session DLP policies decide what an operator can do inside a remote session, and how much evidence is kept.
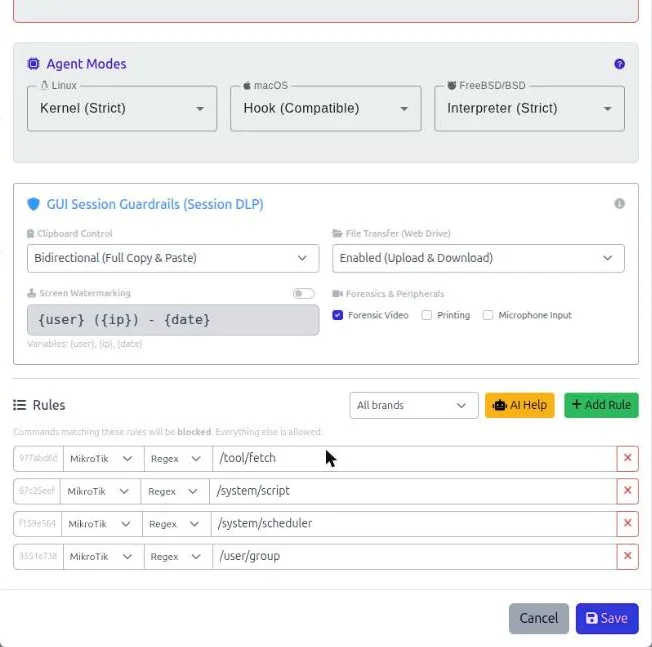
  • ✓ Clipboard and file transfer controlled per policy.
  • ✓ Watermarking on the session, set per policy.
  • ✓ Forensic recording switched on per policy.
MikroWizard PAM policy with session DLP settings for clipboard, file transfer, watermark and forensic video recording
Inspect High-Res Screen

Session DLP Policy: Clipboard, file transfer, watermark and forensic video settings in one policy.

Configurable Data Retention Free + Pro

Choose how long audit and monitoring data is kept; the default is 365 days. Unresolved events and logins that have recordings are always kept, so open issues and recorded sessions are never cleaned up by retention.
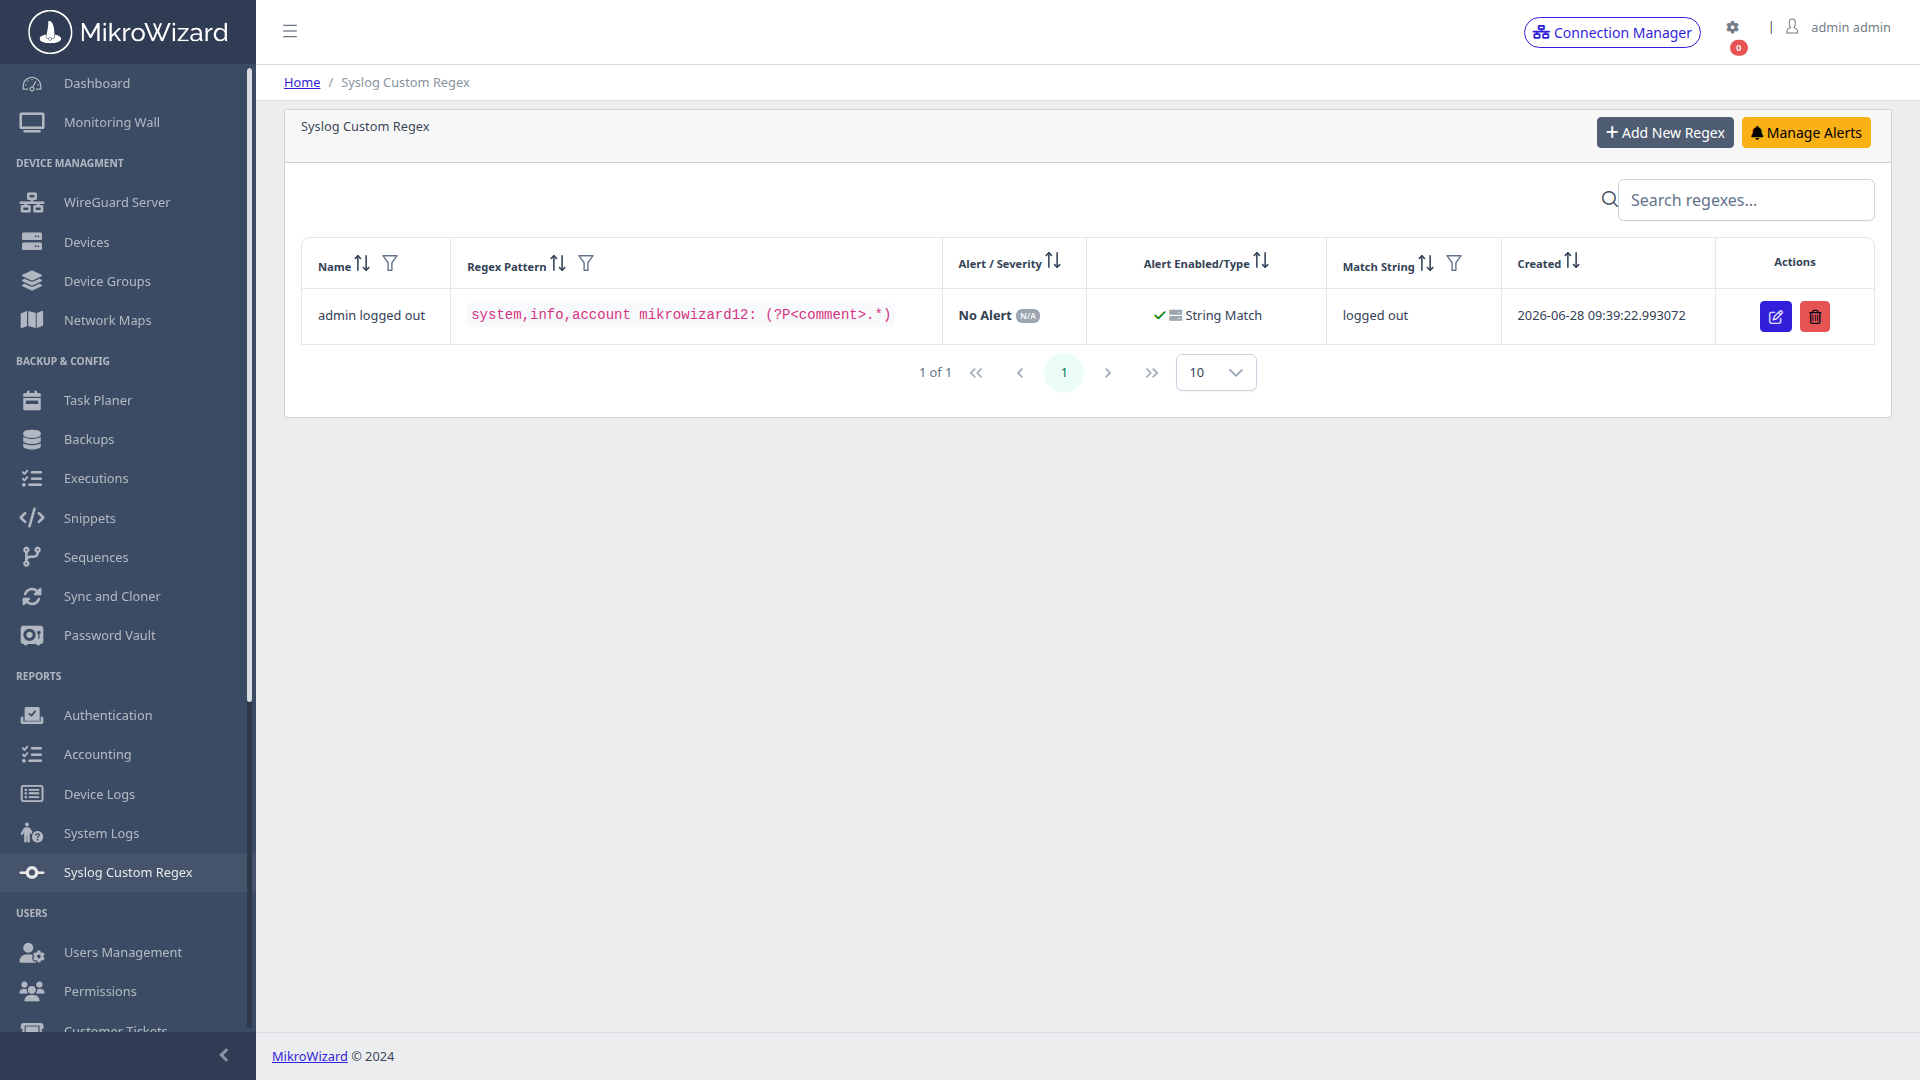
Syslog Regex Classifiers
Inspect High-Res Screen

Regex Pattern Engine: Rule definitions categorizing raw router syslog streams into actionable high-severity events.

Log Analytics

Syslog Regular Expression Pattern Classifiers

Transform millions of noisy router syslog messages into actionable operational insights. Define custom regex patterns to classify critical events:

  • ✓ Pattern Matching: Tag BGP neighbor drops, OSPF link flaps, and firewall brute force attempts automatically.
  • ✓ Syslog History Search: Fast filtered search of syslog history across your device fleet.
Alerting

Multi-Channel Alert Dispatcher (Apprise)

Ensure critical network incidents reach on-call engineers within seconds. MikroWizard integrates Apprise, with 11 built-in channels plus any Apprise URL:
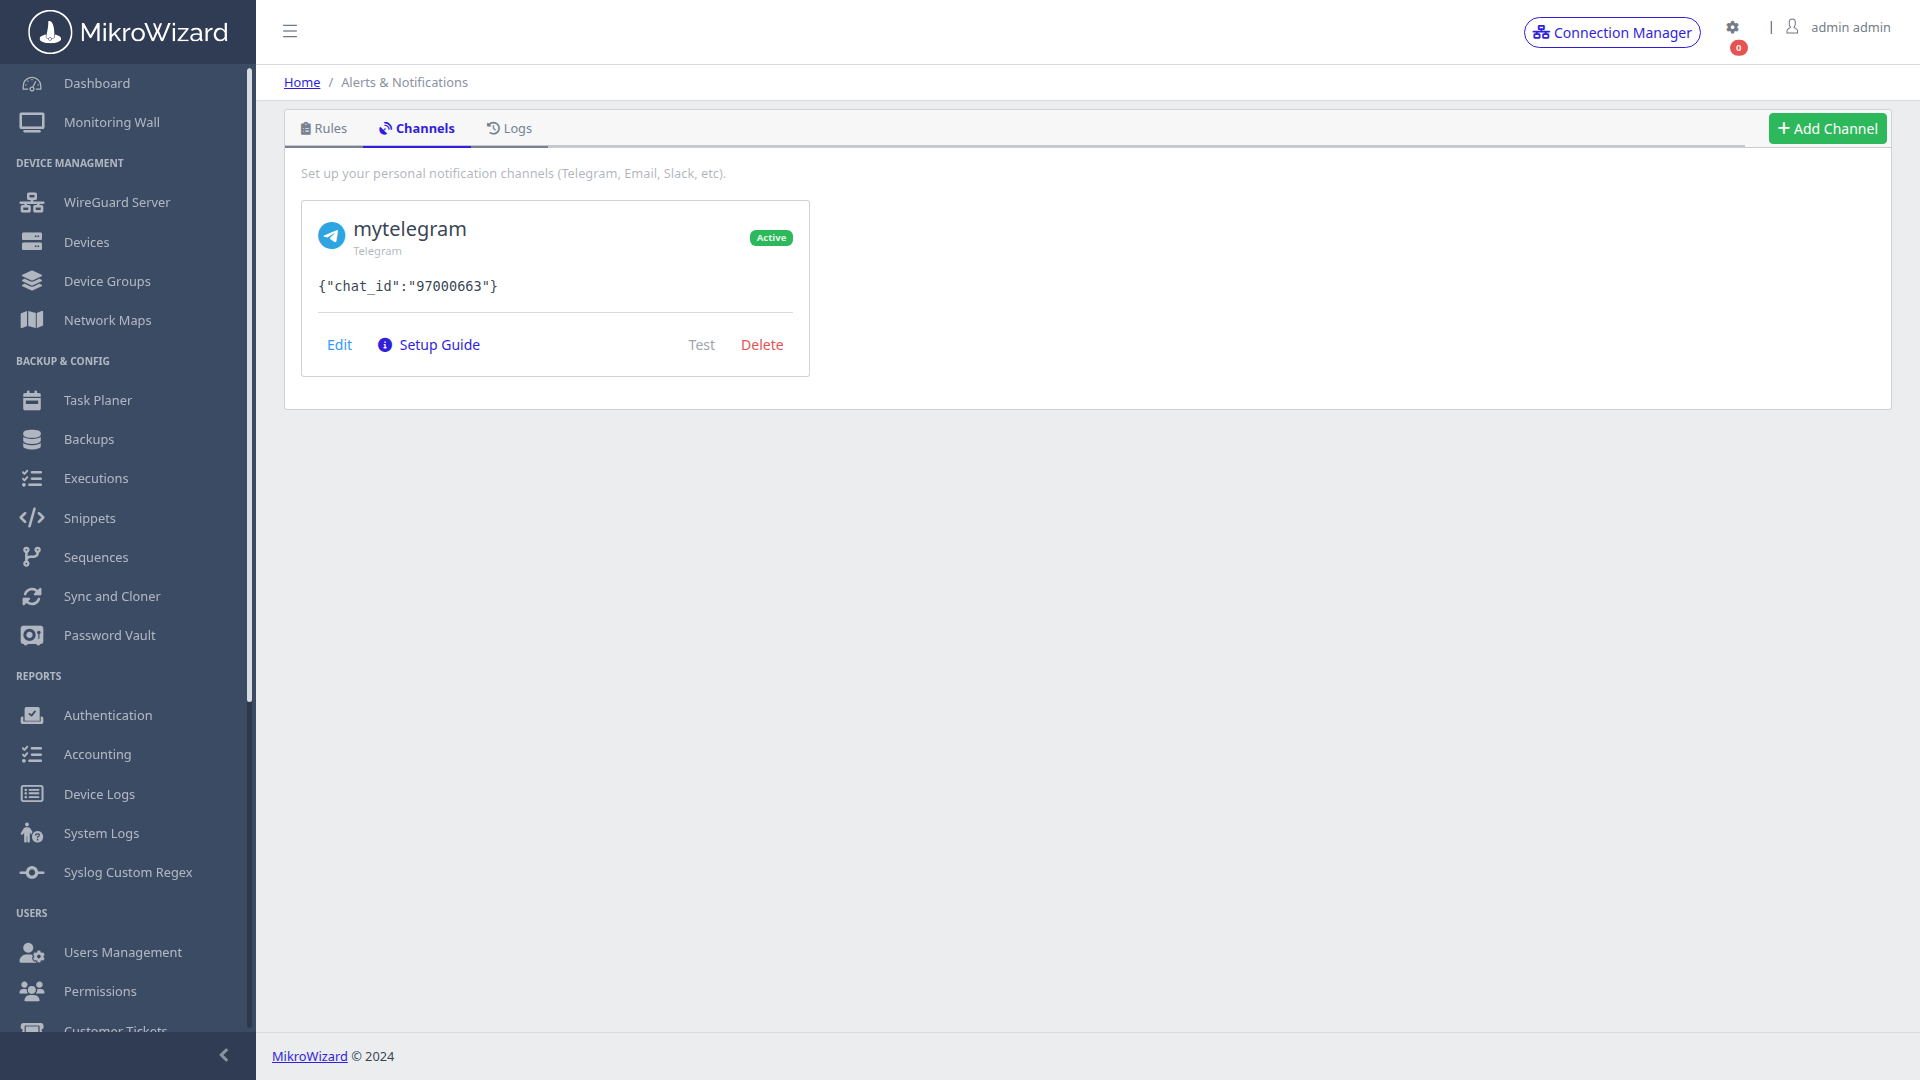
  • ✓ Telegram, Slack, Discord, Pushover, ntfy, Gotify, Mattermost, Microsoft Teams, Opsgenie, PagerDuty and custom Apprise URLs, plus email.
  • ✓ Custom routing rules based on event severity, device group, or time of day.
Apprise Alert Notification Channels
Inspect High-Res Screen

Notification Channels: Configured webhook URLs, chat bot tokens, and active event triggers.

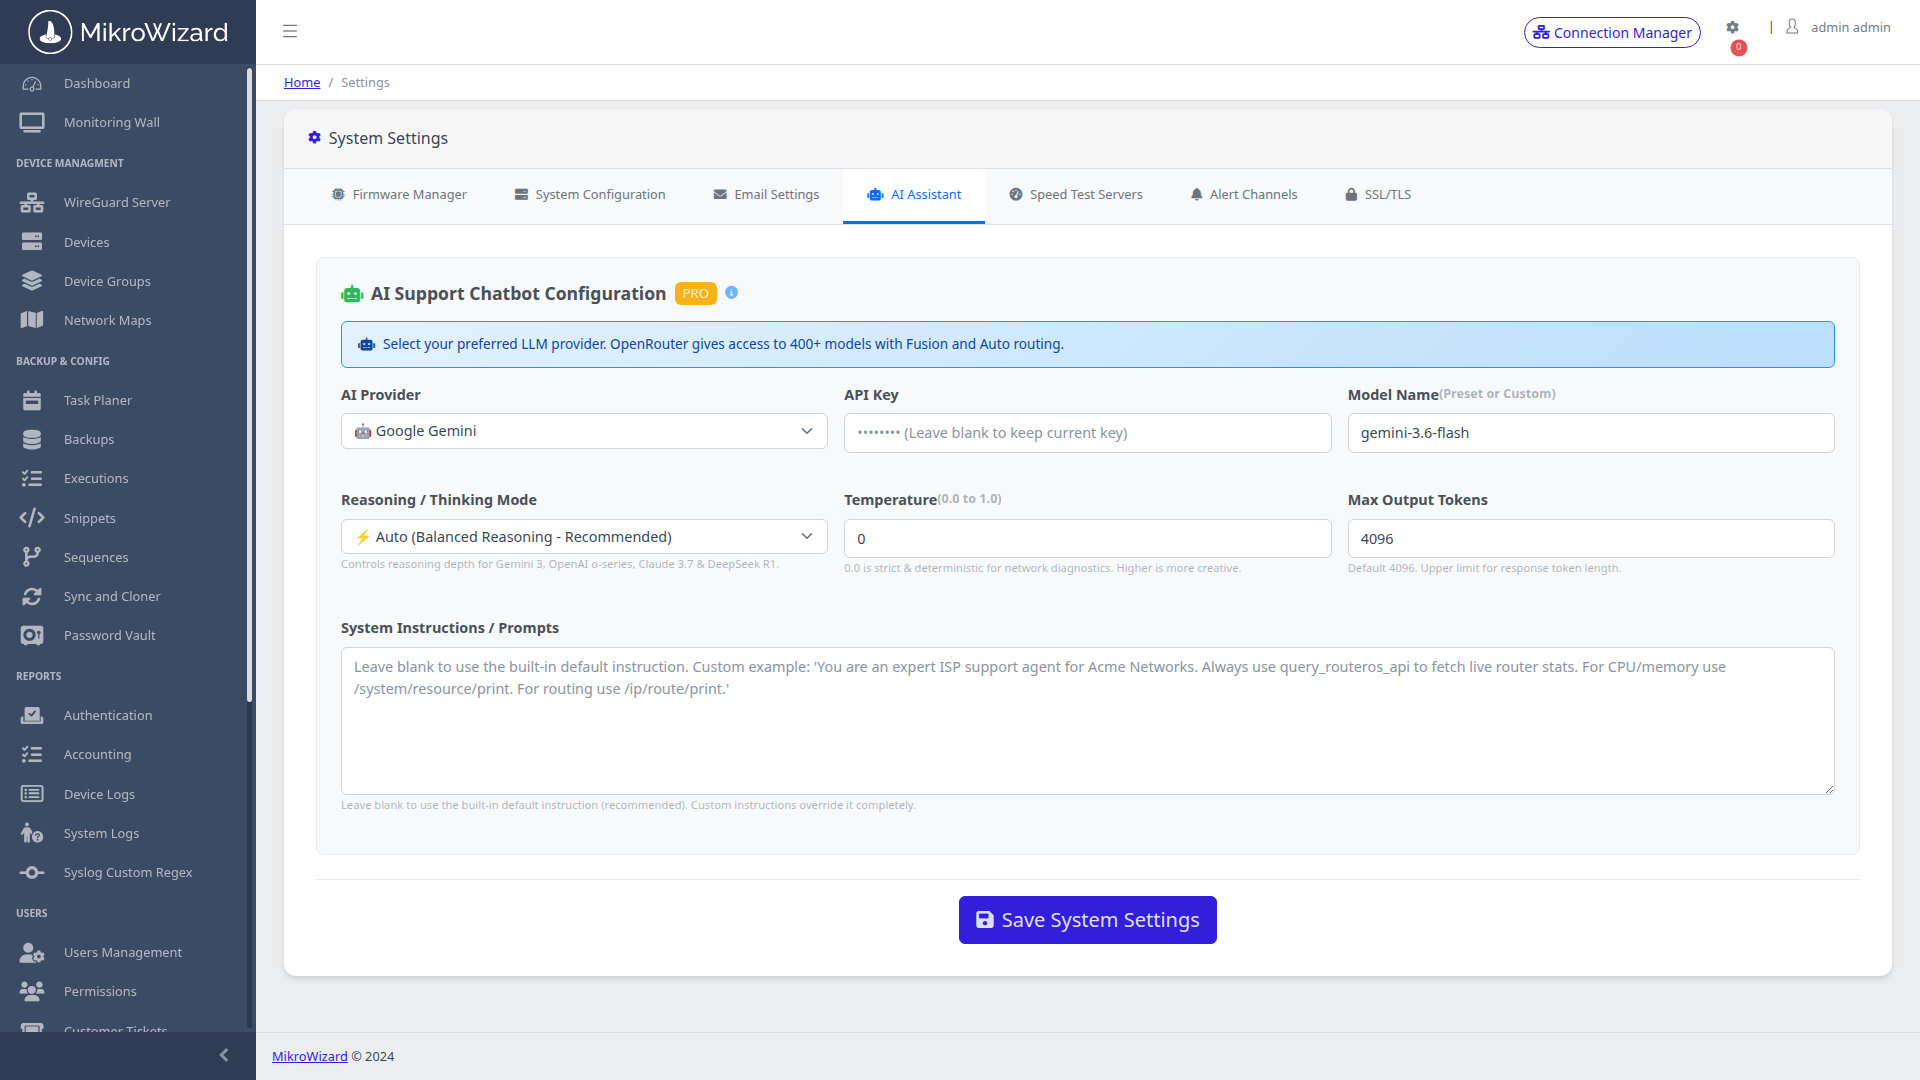
AI Engine Configuration
Inspect High-Res Screen

AI Copilot Settings: Multi-provider LLM connector (Google Gemini, OpenAI, Anthropic Claude, DeepSeek, OpenRouter) with 13 sandboxed tool actions.

Intelligence

Multi-Provider AI Copilot with 13 RouterOS Tool Actions

Accelerate incident root-cause analysis with an AI assistant that understands network topology and RouterOS syntax. Supports Google Gemini, OpenAI, Anthropic Claude, DeepSeek and OpenRouter via a unified LLM abstraction layer.

  • ✓ Multi-Provider LLM: Google Gemini, OpenAI, Anthropic Claude, DeepSeek and OpenRouter — switch providers without code changes.
  • ✓ 13 RouterOS Tool Actions: AI executes sandboxed read-only commands — ping, traceroute, interface stats, routes, speed tests, and RouterOS script generation.
  • ✓ Plain-English Queries: Diagnose outages, generate RouterOS configurations, and analyze logs using natural language — no CLI expertise required.
AI Governance

AI Copilot Compliance Audit Trail & Tool Execution History

Enterprise AI safety, explainability, and governance — every AI interaction is logged in a centralised, searchable audit trail. Satisfy security auditors who need complete visibility into what the AI assistant did, why, and on which routers.
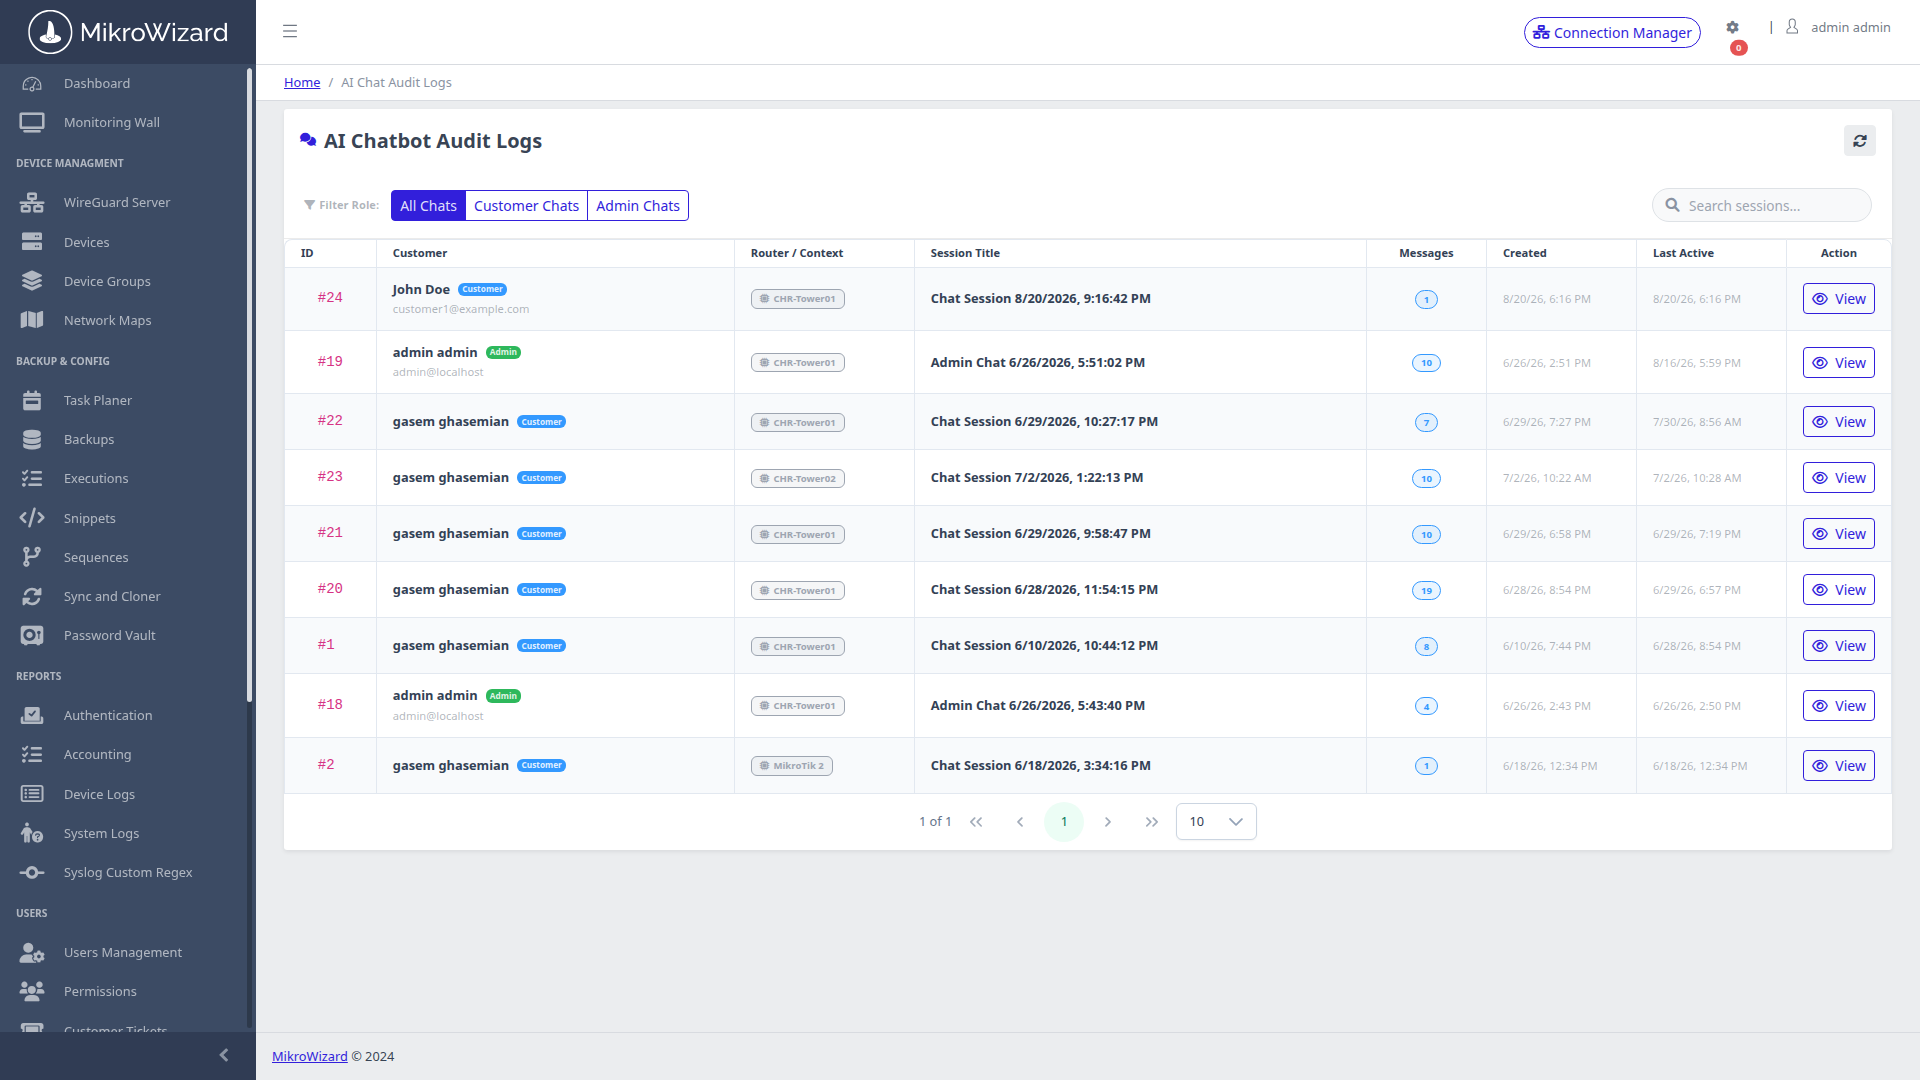
  • ✓ Full Session Logging: Records operator prompts, model responses, every tool call invoked, parameter payloads, and affected device IDs.
  • ✓ Reasoning Explainability: Inspect the AI's decision chain and tool execution tree for any historical session.
  • ✓ ISO 27001 / SOC 2 Evidence: AI governance logs feed directly into compliance evidence packages alongside human operator audit trails.
AI Copilot Audit Logs
Inspect High-Res Screen

AI Audit Trail: Chronological record of AI interactions, tool invocations, parameters, and affected router IDs.

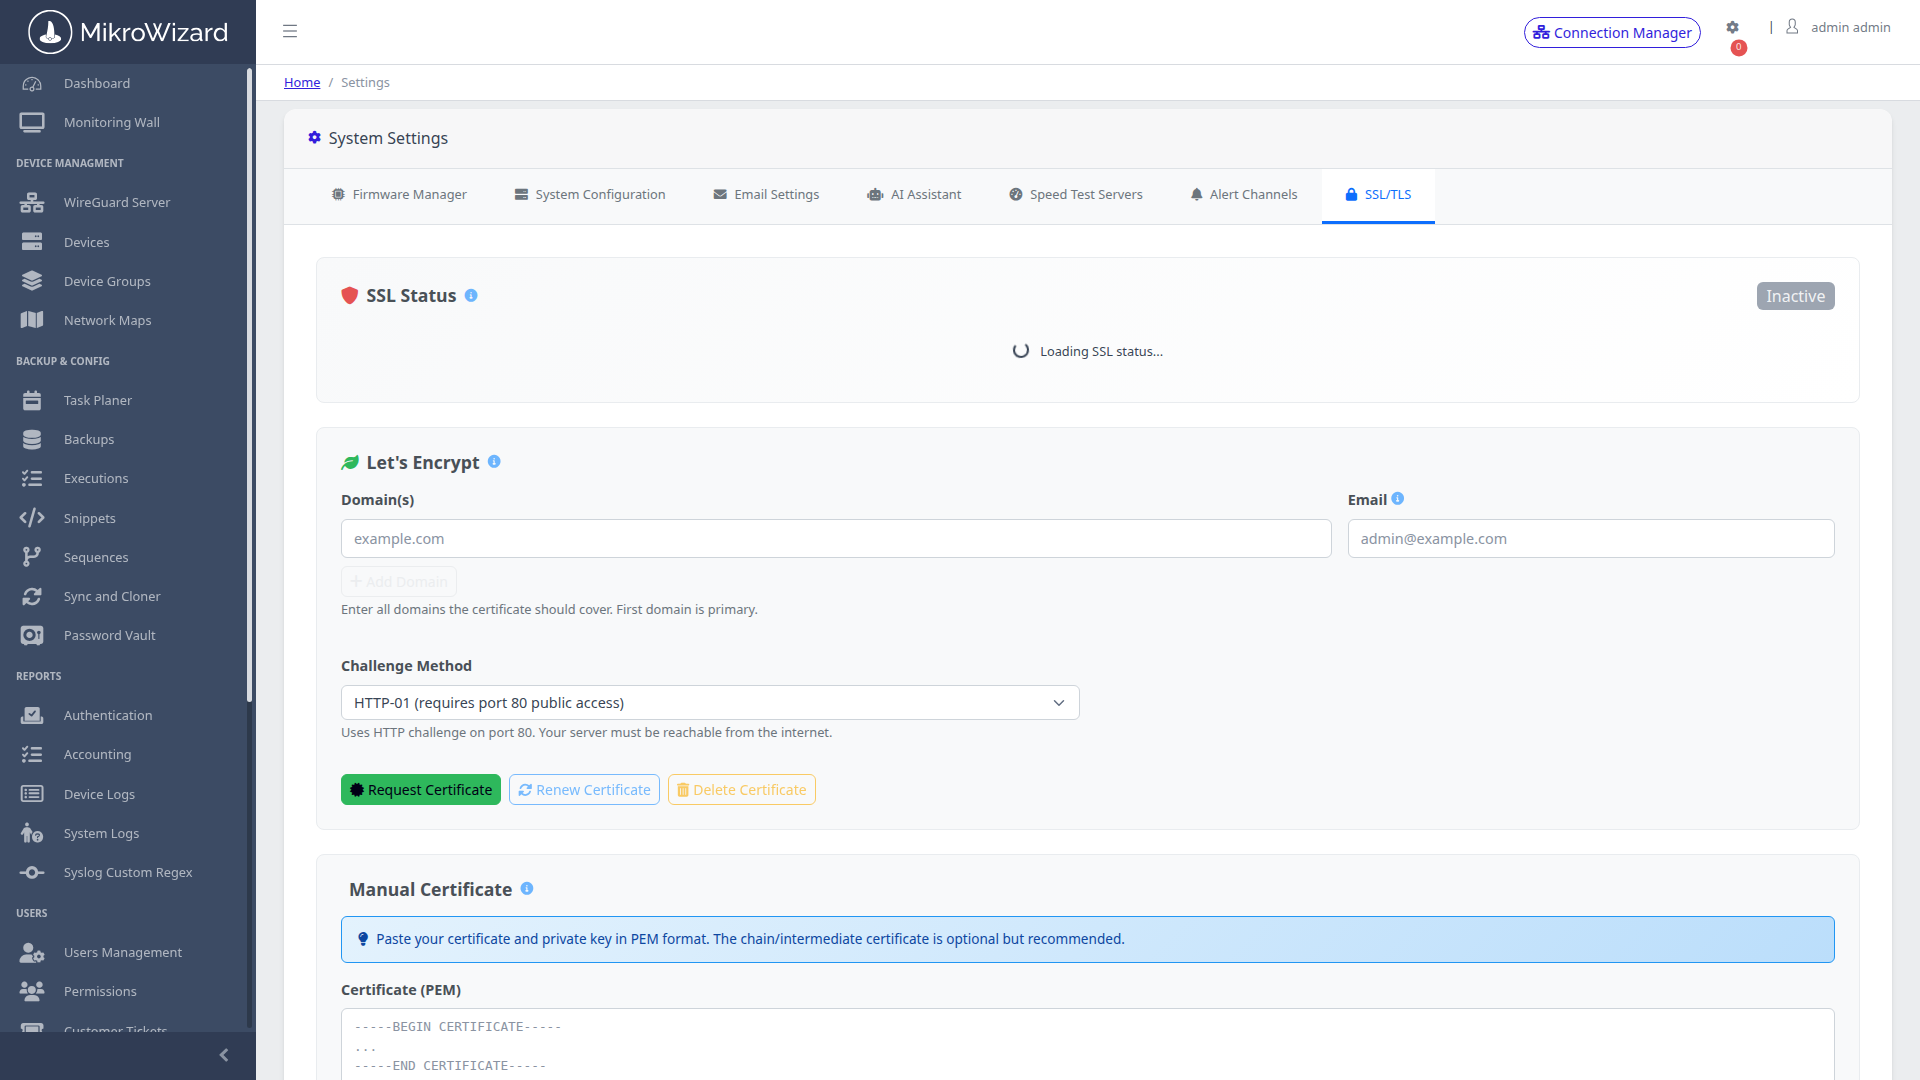
SSL/TLS Certificate Manager
Inspect High-Res Screen

SSL/TLS Manager: Automated Let's Encrypt ACME HTTP-01 challenge flow and custom PEM certificate upload.

System Infrastructure

Automated Let's Encrypt SSL/TLS Certificate Provisioning

Zero-touch HTTPS encryption for the entire management portal. MikroWizard automates the ACME HTTP-01 challenge verification for Let's Encrypt certificates, eliminating manual renewal headaches.

  • ✓ Auto-Renewal Timers: Certificates renew automatically before expiry — no crontab or manual intervention required.
  • ✓ Custom PEM Upload: Supports manual upload of corporate or wildcard certificates with private key validation.
  • ✓ HTTPS Everywhere: Enforces encrypted transport for admin panel, subscriber portal, and all API endpoints.
System Infrastructure

SMTP Email Dispatcher & Notification Server Settings

Reliable automated email delivery for critical network alerts, administrative password recovery, and audit report distribution via configurable SMTP relay.
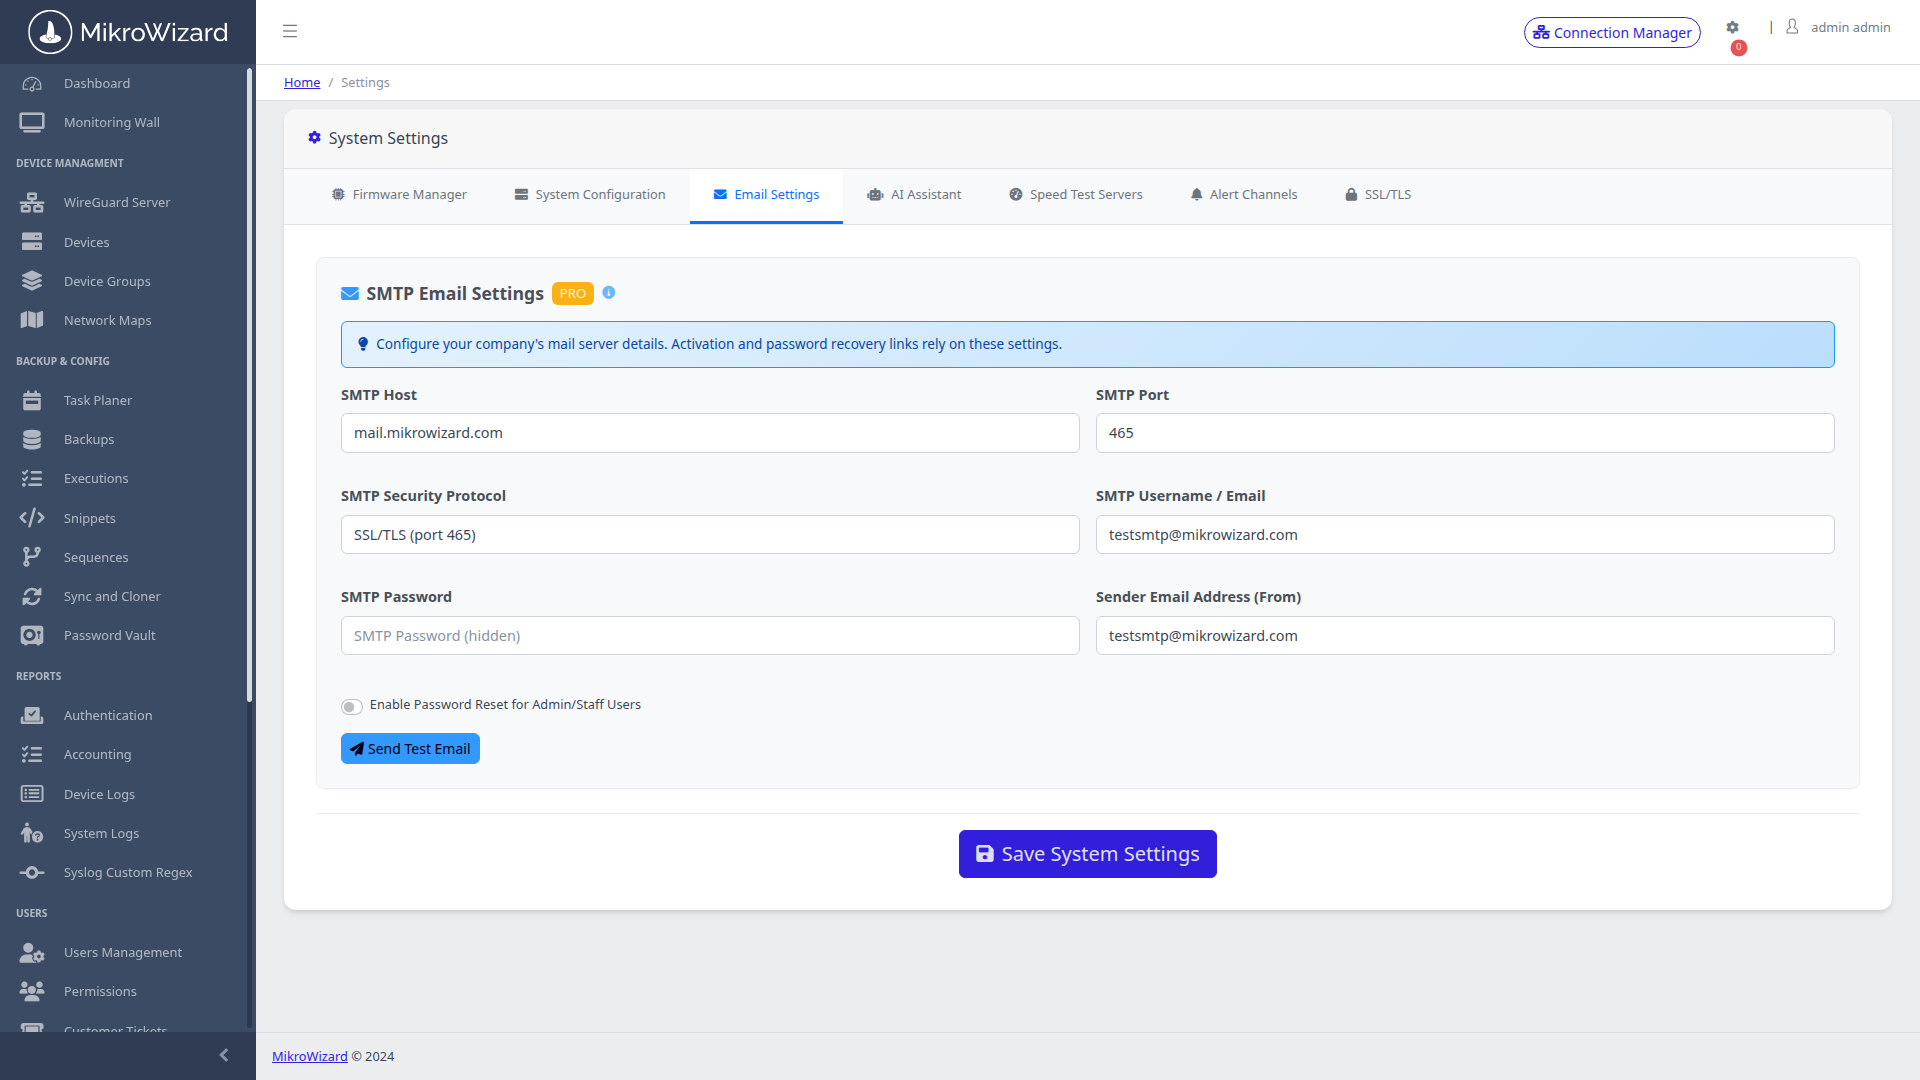
  • ✓ SSL/TLS Support: STARTTLS and SSL/TLS on port 465/587 with custom sender addresses and authentication credentials.
  • ✓ Live Test Email: Interactive test dispatcher to verify SMTP relay configuration without triggering production alerts.
  • ✓ Alert Routing: Powers device-offline email alerts, backup failure notifications, and system event digests.
SMTP Email Configuration
Inspect High-Res Screen

SMTP Settings: SSL/TLS relay configuration with live test email dispatcher and sender address management.

Audit Compliant

Prepare for Network Security Audits with MikroWizard

Deploy on-premises. Maintain 5-tier forensic logs, regex syslog classifiers, and AI auditability.
Request Live Architecture Demo Explore Pricing Plans